Black Friday Rush: 75% Off All Exam Bundles! Apply the coupon code below before the offer expires! - Ends in 0d 00h 00m 00s - Coupon code: newyear

Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2

Page: 4 / 14
Total 444 questions

An engineer is troubleshooting connectivity to the DNS servers from hosts behind a new Cisco FTD device. The hosts cannot send DNS queries to servers in the DMZ. Which action should the engineer take to troubleshoot this issue using the real DNS packets?

A.

Use the Connection Events dashboard to check the block reason and adjust the inspection policy as needed.

B.

Use the packet capture tool to check where the traffic is being blocked and adjust the access control or intrusion policy as needed.

C.

Use the packet tracer tool to determine at which hop the packet is being dropped.

D.

Use the show blocks command in the Threat Defense CLI tool and create a policy to allow the blocked traffic.

A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FMC. An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?

A.

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.

B.

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.

C.

Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the " Drop when inline " option.

D.

Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the " Drop when inline " option.

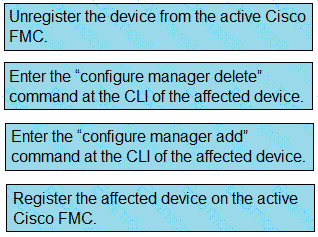
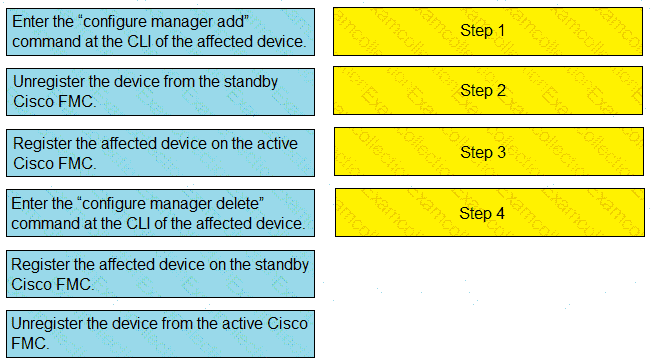
Drag and drop the steps to restore an automatic device registration failure on the standby Cisco FMC from the left into the correct order on the right. Not all options are used.
An organization is setting up two new Cisco FTD devices to replace their current firewalls and cannot have any network downtime During the setup process, the synchronization between the two devices is failing What action is needed to resolve this issue?

A.

Confirm that both devices have the same port-channel numbering

B.

Confirm that both devices are running the same software version

C.

Confirm that both devices are configured with the same types of interfaces

D.

Confirm that both devices have the same flash memory sizes

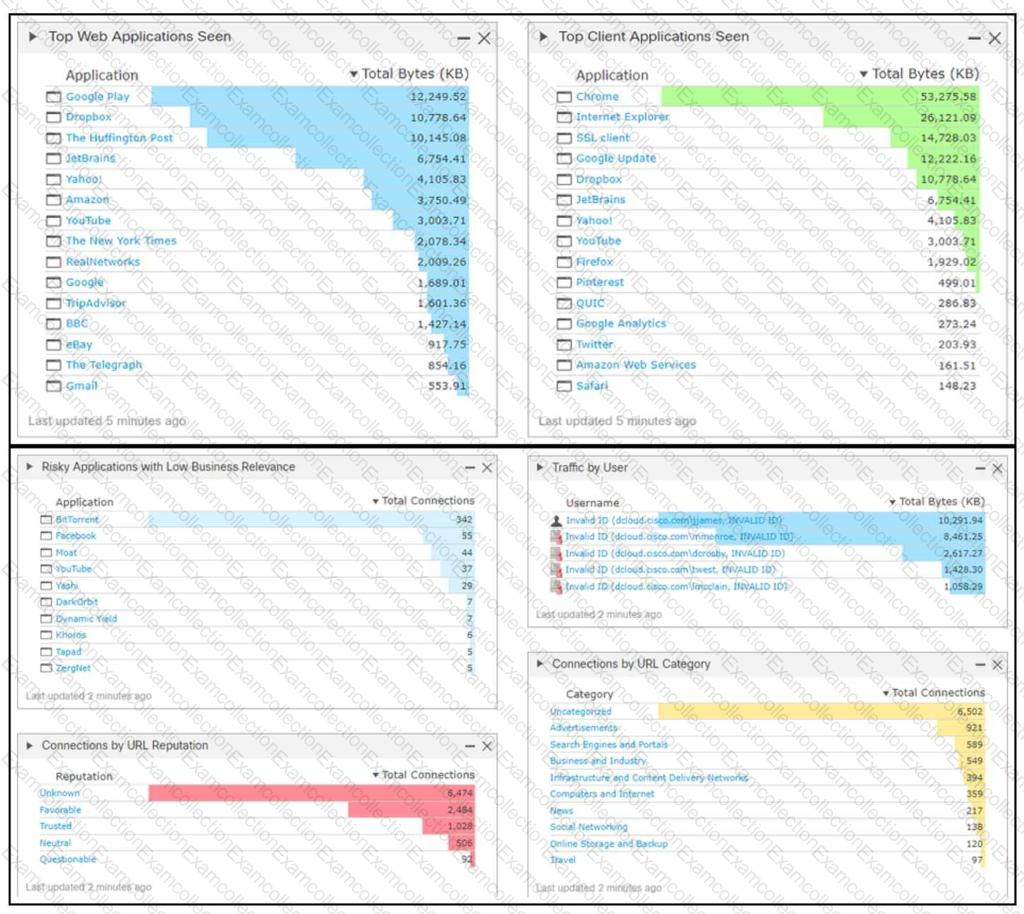
Refer to the exhibit.

An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must the engineer take to decrease the application usage risk?

A.

Disable the use of Google Play.

B.

Disable the user account.

C.

Block all the BitTorrent applications.

D.

Patch all the Google Chrome browsers.

An engineer is reviewing an existing custom server fingerprint on a Cisco Secure Firewall because the current information is inaccurate. Which action must the engineer take to improve the accuracy of the network discovery rules?

A.

Exclude the IP address that is used to communicate with the monitored host.

B.

Exclude the ports that must be skipped.

C.

Add NetFlow monitoring for the network segment.

D.

Set one common rule to override the reports in the multidomain environment.

A security engineer is adding three Cisco FTD devices to a Cisco FMC. Two of the devices have successfully registered to the Cisco FMC. The device that is unable to register is located behind a router that translates all outbound traffic to the router ' s WAN IP address. Which two steps are required for this device to register to the Cisco FMC? (Choose two.)

A.

Reconfigure the Cisco FMC lo use the device ' s private IP address instead of the WAN address.

B.

Configure a NAT ID on both the Cisco FMC and the device.

C.

Add the port number being used for PAT on the router to the device ' s IP address in the Cisco FMC.

D.

Reconfigure the Cisco FMC to use the device ' s hostname instead of IP address.

E.

Remove the IP address defined for the device in the Cisco FMC.

An engineer is configuring a Secure Firewall Threat Defense device to replace an existing Cisco ASA in the network. The Cisco ASA has rate-limiting policies and dynamic routing in place on the interfaces that must be duplicated on the Secure Firewall Threat Defense configuration. How must the engineer deploy the Cisco Secure Firewall to allow the duplication?

A.

routed mode with routed interfaces

B.

routed mode with bridge groups

C.

transparent mode with bridge groups

D.

transparent mode with subinterfaces

A connectivity issue is occurring between a client and a server which are communicating through a Cisco Firepower device While troubleshooting, a network administrator sees that traffic is reaching the server, but the client is not getting a response Which step must be taken to resolve this issue without initiating traffic from the client?
A.

Use packet-tracer to ensure that traffic is not being blocked by an access list.

B.

Use packet capture to ensure that traffic is not being blocked by an access list.

C.

Use packet capture to validate that the packet passes through the firewall and is NATed to the corrected IP address.

D.

Use packet-tracer to validate that the packet passes through the firewall and is NATed to the corrected IP address.

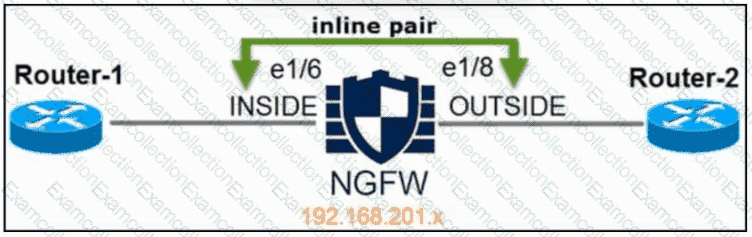
Refer to the exhibit. An engineer is configuring an instance of Cisco Secure Firewall Threat Defense with interfaces in IPS Inline Pair mode. What must be configured on interface e1/6 to accomplish the requirement?

A.

propagate link state disabled

B.

inline set MTU set to 1500

C.

FailSafe disabled

D.

security zone set to OUTSIDE_ZONE