Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: newyear

Fortinet NSE6_EDR_AD-7.0 - Fortinet NSE 6 - FortiEDR 7.0 Administrator

Page: 1 / 1
Total 35 questions

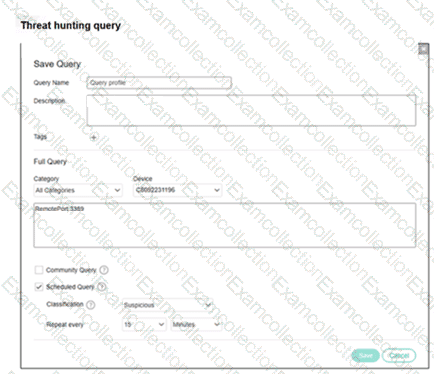
Refer to the exhibit.

Based on the exhibit, which statement about this threat hunting query is true? (Choose one answer)

A.

A security incident will be generated whenever the device attempts an RDP connection.

B.

The query is limited to detecting network activity and does not inspect process behavior.

C.

The query is configured as a global hunting rule and is automatically visible across all organizations.

D.

RDP connections will be automatically blocked and classified as suspicious.

A collector attempts to access a known malicious website. FortiEDR is configured for eXtended detection with FortiAnalyzer. What two roles does Fortinet Cloud Services (FCS) perform in this process? (Choose two answers)

A.

FCS sends a log record to FortiAnalyzer.

B.

FCS sends OS metadata to the FortiEDR manager.

C.

FCS correlates and analyzes the collected logs.

D.

FCS identifies if a malicious event has taken place and reports the detection incident.

A playbook is configured with two actions: terminate process and isolate device. The terminate process action fails because the process is protected by Windows. What is the expected behavior for the second action, isolate device? (Choose one answer)

A.

The playbook execution pauses and requires administrator intervention.

B.

The playbook generates a notification email and execution stops.

C.

The playbook execution stops because the action fails.

D.

The playbook continues and executes the second action.

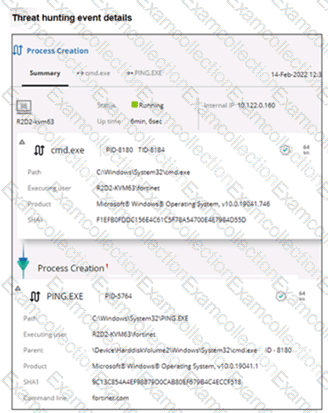
Refer to the exhibit.

Based on the threat hunting event details shown in the exhibit, which two statements about the event are true? (Choose two answers)

A.

There are no MITRE details available for this event.

B.

The activity event is associated with the file action.

C.

The PING.EXE process was blocked.

D.

The user fortinet has executed a ping command.

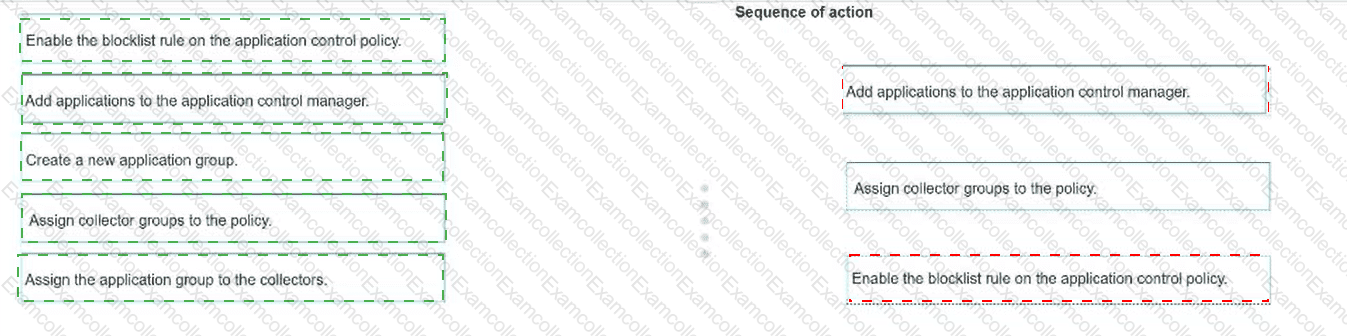
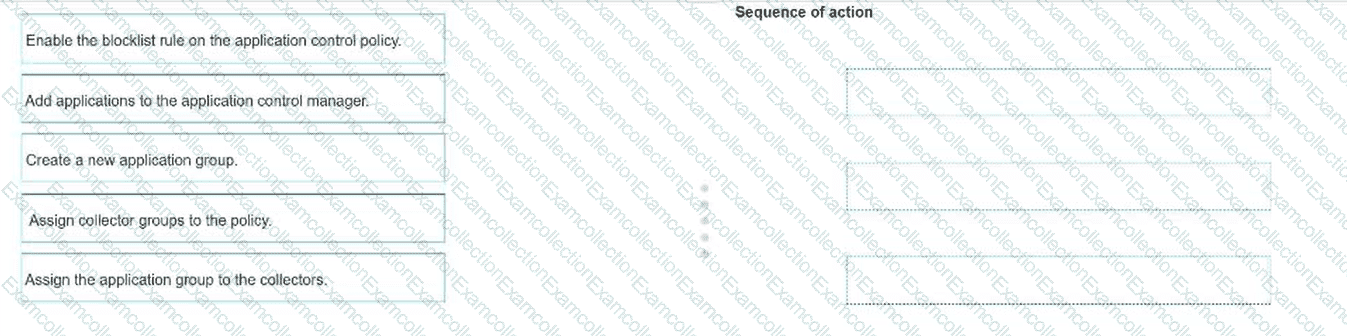
When implementing an application block policy in FortiEDR, which three actions, in order, reflect the correct operational sequence? (Choose three.)

Select an action in the left column and hold and drag it to a blank position in the column on the right. Place the three correct actions in order, starting with the first action at the top of the column. After you

place an action, you can move it again if you want to change your answer before proceeding to the next question. You must drop three actions in the work area.

Select and drag the screen divider to change the viewable area of the source and work areas.
Refer to the Exhibit:
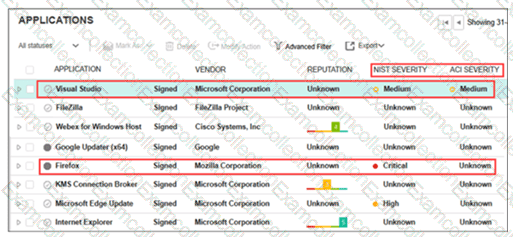
A FortiEDR analyst is prioritizing response efforts. One application has a vulnerability score of Critical but an Unknown ACI rating, while another has a Medium vulnerability score with active ACI evidence of adversary targeting. Which application must be addressed first? (Choose one answer)

A.

Both applications should be treated equally because patching is necessary.

B.

The application with the Critical vulnerability score should be addressed first.

C.

The decision depends only on asset criticality, not scores.

D.

The application with the Medium vulnerability score and ACI evidence should be addressed first.

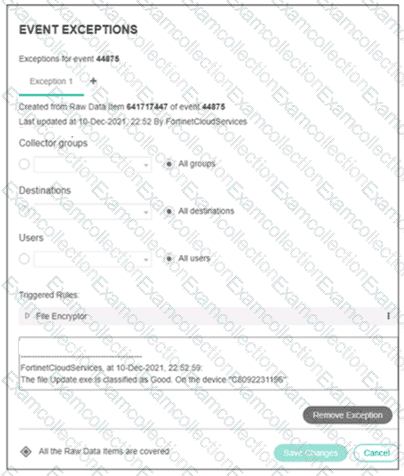
Refer to the exhibit.

An event exception is shown. Which two statements about the exception are true? (Choose two answers)

A.

A partial exception is applied to this event.

B.

The exception is applied only on device C8092231196.

C.

The system owner can modify the trigger rules parameters.

D.

FCS playbooks are enabled by Fortinet support.

Which two statements correctly describe the IoT probing process on FortiEDR? (Choose two answers)

A.

Collectors running on servers are always used for IoT probing.

B.

It identifies nearby devices by retrieving details such as hostname and IP address.

C.

Only healthy collectors participate in IoT probing.

D.

It captures all traffic from neighboring devices for deep packet inspection.

Within the FortiEDR architecture, which component needs JumpBox capabilities to enable authenticated and controlled communication with FortiAnalyzer? (Choose one answer)

A.

Core

B.

Central manager

C.

Aggregator

D.

Reputation Server

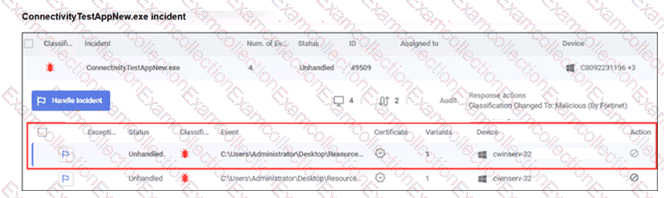
Refer to the exhibit.

What observation can you make about the ConnectivityTestAppNew.exe incident? (Choose one answer)

A.

A rule assigned action is set to block but the policy is in simulation mode.

B.

The incident has not been handled by a console administrator.

C.

The incident was archived from the console unhandled.

D.

The incident was handled automatically by the communication control policy.