Black Friday Rush: 75% Off All Exam Bundles! Apply the coupon code below before the offer expires! - Ends in 0d 00h 00m 00s - Coupon code: newyear

Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2

Page: 13 / 14
Total 444 questions

An engineer is implementing clustering in Cisco Secure Firewall Management Center. The configuration must ensure that the cluster has a designated control node with more resources than the other nodes. What must the engineer set for the priority value of that node?

A.

0

B.

A value lower than the values assigned to the other nodes in the cluster

C.

A value higher than the values assigned to the other nodes in the cluster

D.

255

In which two ways do access control policies operate on a Cisco Firepower system? (Choose two.)

A.

Traffic inspection can be interrupted temporarily when configuration changes are deployed.

B.

The system performs intrusion inspection followed by file inspection.

C.

They can block traffic based on Security Intelligence data.

D.

File policies use an associated variable set to perform intrusion prevention.

E.

The system performs a preliminary inspection on trusted traffic to validate that it matches the trusted parameters.

A network administrator cannot select the link to be used for failover when configuring an active/passive HA Cisco FTD pair.

Which configuration must be changed before setting up the high availability pair?

A.

An IP address in the same subnet must be added to each Cisco FTD on the interface.

B.

The interface name must be removed from the interface on each Cisco FTD.

C.

The name Failover must be configured manually on the interface on each cisco FTD.

D.

The interface must be configured as part of a LACP Active/Active EtherChannel.

An engineer is configuring URL filtering for a Cisco FTD device in Cisco FMC. Users must receive a warning when they access http:/ ' www.Dac ' additstte.corn with the option of continuing to the website if they choose to. No other websites should be blacked. Which two actions must the engineer lake to meet these requirements? (Choose two.)

A.

On the HTTP Responses tab of the access control policy editor, set the Block Response Page to Custom.

B.

On the HTTP Responses tab of the access control policy editor, sot the Interactive Block Response Page to system-provided.

C.

Configure the default action for the access control policy to Interactive Block.

D.

Configure an access control rule that matches the Adult URL category and se: the action to interactive Block.

E.

Configure an access control rule that matches an URL object for http://www.badaduitslte.com; and set the action to interactive Block.

Refer to the exhibit.

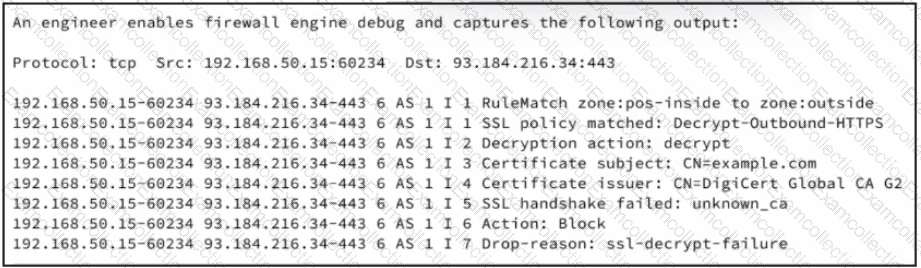
Security engineer is investigating an issue where outbound HTTPS traffic from an endpoint using network 192.168.50.0/24 is being blocked. The Cisco Secure Firewall Threat Defense is configured with a TLS decryption policy applied to all outbound web traffic. An engineer enables firewall engine debug and captures the output. Which action must be performed to resolve the issue?

A.

Export the TLS re-signing CA certificate used by the SSL policy and deploy it to the trusted root store on the POS terminals.

B.

Enroll the FTD re-signing CA from the corporate internal CA and redeploy the SSL policy, trusted in the Windows certificate store.

C.

Add DigiCert Global CA G2 to the trusted CA list in the SSL policy to accept the external issuer during re-signing and complete the handshake.

D.

Add the destination IP range of POS terminal traffic to a URL-category-based SSL rule with the action set to Do Not Decrypt.

A network administrator is reviewing a weekly scheduled attacks risk report and notices a host that is flagged for an impact 2 attack. Where should the administrator look within Cisco FMC to find out more relevant information about this host and attack?
A.

Analysis > Lookup > Whols

B.

Analysis > Correlation > Correlation Events

C.

Analysis > Hosts > Vulnerabilities

D.

Analysis > Hosts > Host Attributes

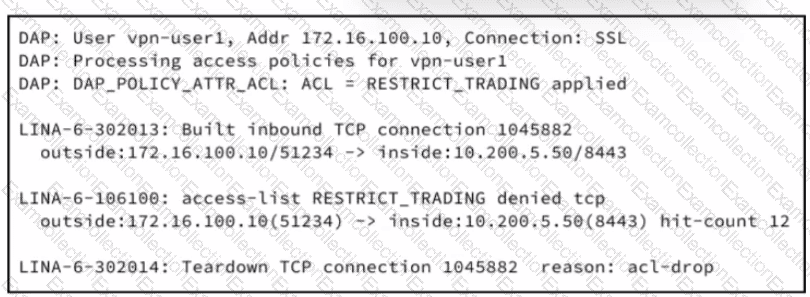
Refer to the exhibit. Authenticated VPN users at a financial institution can reach trading servers in the 10.200.0.0/16 range, but one user, vpn-useM is not able to access the trading application at 10.200.5.50 on TCP 8443. An engineer enables system support trace on the Cisco Secure Firewall Threat Defense. Which action must be performed to resolve the issue?

A.

Modify the group policy to assign a higher-privilege VPN filter ACL to all users in vpn-user1 ' s group, overriding the ACL applied by DAP.

B.

Edit the group policy for the VPN tunnel group and permit 10.200.5.50/8443 in the split-tunnel ACL.

C.

Update the DAP RESTRICT_TRADING ACL to permit TCP to 10.200.5.50 on port 8443.

D.

Add a static route for 10.200.5.0/24 pointing to the inside interface, and a static route for the vpn-user1 host 172.16.100.10 to the outside interface.

Which action should be taken after editing an object that is used inside an access control policy?

A.

Delete the existing object in use.

B.

Refresh the Cisco FMC GUI for the access control policy.

C.

Redeploy the updated configuration.

D.

Create another rule using a different object name.

An engineer is configuring a custom intrusion rule on Cisco FMC. The engineer needs the rule to search the payload or stream for the string " |45 5* 26 27 4 0A|*. Which Keyword must the engineer use with this stung lo create an argument for packed inspection?

A.

metadata

B.

Content

C.

Protected _ content

D.

data

An engineer is configuring a new dashboard within Cisco Secure Firewall Management Center and is having trouble implementing a custom widget. When a custom analysis widget is configured which option is mandatory for the system to display the information?

A.

table

B.

filter

C.

title

D.

results