Cisco 300-715 - Implementing and Configuring Cisco Identity Services Engine (SISE) v1.1 (300-715 SISE)
Refer to the exhibit.
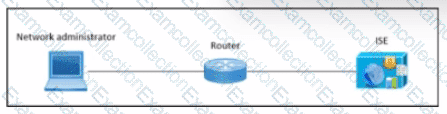
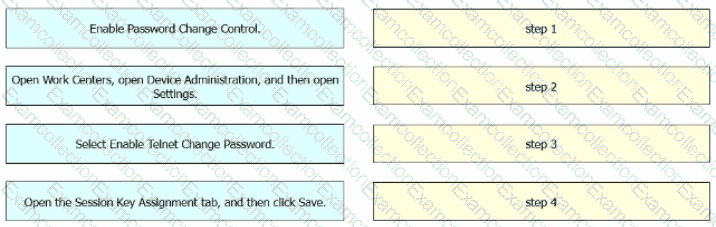
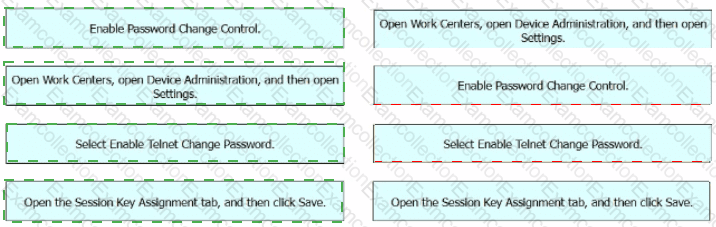
An engineer must configure Cisco ISE to be used as the TACACS+ server for any administrator that signs into the router. Users must be able to change their Telnet password through the TACACS+ server. Drag and drop the configuration steps from the left into the sequence on the right.
Which two features are available when the primary admin node is down and the secondary admin node has not been promoted? (Choose two.)
Refer to the exhibit.
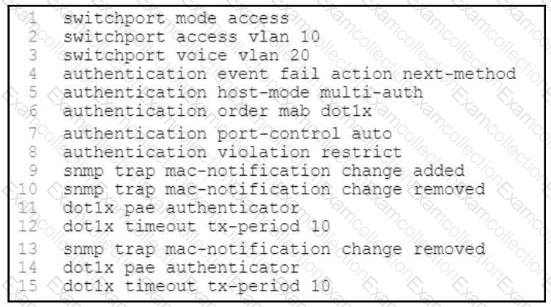
An engineer is deploying 802.1X in a network that contains printers that do not support 802.1X. The current Cisco IOS switch-port configuration is shown in the exhibit. Which additional command is needed to allow the printers to authenticate?
A user is attempting to register a BYOD device to the Cisco ISE deployment, but needs to use the onboarding policy to request a digital certificate and provision the endpoint. What must be configured to accomplish this task?
A network administrator must configure Cisco SE Personas in the company to share session information via syslog. Which Cisco ISE personas must be added to syslog receivers to accomplish this goal?
An administrator replaced a PSN in the distributed Cisco ISE environment. When endpoints authenticate to it, the devices are not getting the right profiles or attributes and as a result, are not hitting the correct policies. This was working correctly on the previous PSN. Which action must be taken to ensure the endpoints get identified?
A network engineer is configuring a Cisco Wireless LAN Controller in order to find out more information about the devices that are connecting. This information must be sent to Cisco ISE to be used in authorization policies. Which profiling mechanism must be configured in the Cisco Wireless LAN Controller to accomplish this task?
An organization is hosting a conference and must make guest accounts for several of the speakers attending. The conference ended two days early but the guest accounts are still being used to access the network. What must be configured to correct this?
In a Cisco ISE split deployment model, which load is split between the nodes?
A Cisco ISE administrator must authenticate users against Microsoft Active Directory. The solution must meet these requirements:
Users and computers must be authenticated.
User groups must be retrieved during authentication.
Which protocol must be added to the allowed protocols on the policy to authenticate the users?