Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?
An MDM provides which two advantages to an organization with regards to device management? (Choose two)
Refer to the exhibit.
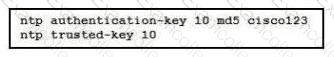
A network engineer is testing NTP authentication and realizes that any device synchronizes time with this router and that NTP authentication is not enforced What is the cause of this issue?
After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?
Refer to the exhibit.
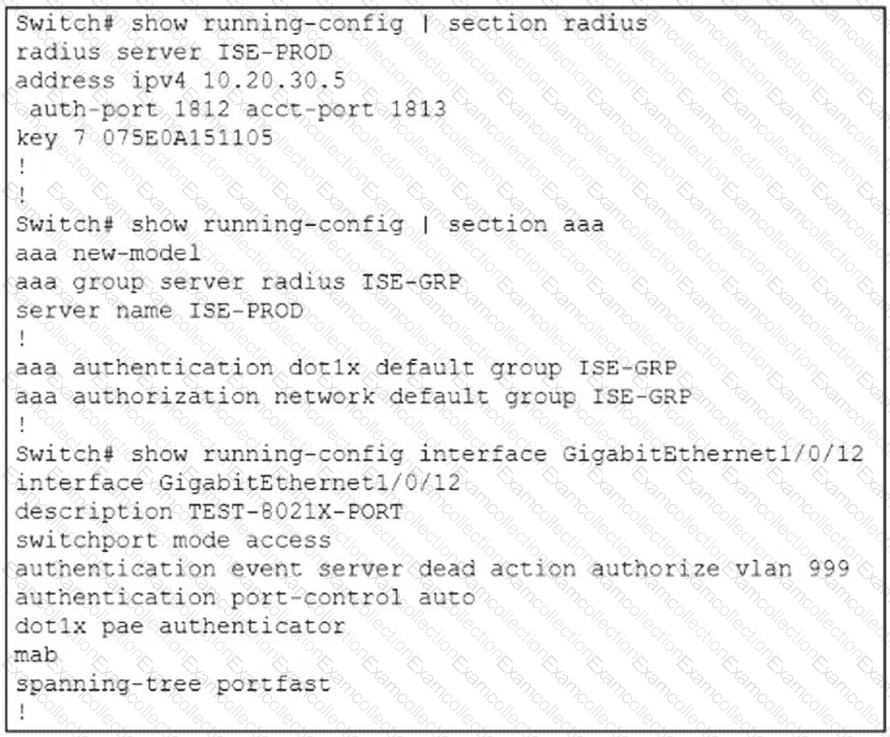
A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown†and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?
An organization plans to upgrade its current email security solutions, and an engineer must deploy Cisco Secure Email. The requirements for the upgrade are:
Implement Data Loss Prevention
Implement mail encryption
Integrate with an existing Cisco IronPort Secure Email Gateway solution
Which Cisco Secure Email license is needed to accomplish this task?
With regard to RFC 5176 compliance, how many IETF attributes are supported by the RADIUS CoA feature?
In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)
Which technology provides the benefit of Layer 3 through Layer 7 innovative deep packet inspection,
enabling the platform to identify and output various applications within the network traffic flows?
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,
data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity
platform. What should be used to meet these requirements?
Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?
After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.
Which task can you perform to determine where each message was lost?
Refer to the exhibit.
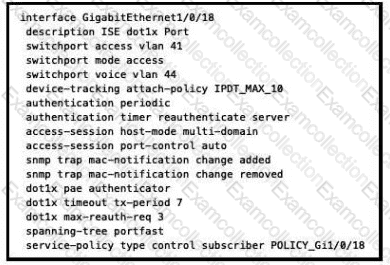
What will occur when this device tries to connect to the port?
Which function is performed by certificate authorities but is a limitation of registration authorities?
Which two conditions are prerequisites for stateful failover for IPsec? (Choose two)