


CompTIA CS0-004 - CompTIA Cybersecurity Analyst CySA+ V4 (New Version)
Which of the following is the most important component to include in the preparation phase of an incident response plan?
A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team.
The analyst must:
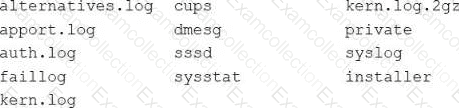
Identify Linux systems that have successful and unsuccessful logins with username "User1".
Create an output report named "linux-events" of all the events to a flat file.
The analyst issues the following console command:
ls /var/log/
The shortened output of the command is below:
Which of the following commands should the analyst use to meet the report output requirements?
Which of the following does a phishing campaign click rate measure?
A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
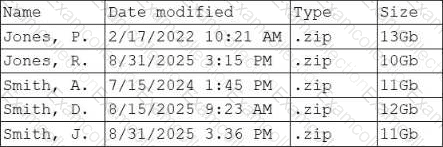
Which of the following actions should the analyst take first?
