


Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmas50

CompTIA CS0-004 - CompTIA Cybersecurity Analyst CySA+ V4 (New Version)

Page: 1 / 3
Total 82 questions

A security analyst uses a full pcap solution to extract all traffic from the last two days associated with the 10.213.4.27 file server.

This file server is under investigation due to concerns about potential data exfiltration using Domain Name System (DNS) traffic.

Which of the following commands should the analyst use to extract any potentially leaked data from the suspicious.pcap file?

A.

strings suspicious.pcap | grep 10.213.4.27

B.

zeek -r suspicious.pcap; grep 10.213.4.27 file.log

C.

snort -r suspicious.pcap; grep eve.log 10.213.4.27

D.

tcpdump -r suspicious.pcap port 53 and host 10.213.4.27

A vulnerability analyst runs a credentialed vulnerability scan covering all addressable enterprise assets. After running the scan, the analyst discovers a large number of critical vulnerabilities that cannot be immediately remediated.

Which of the following are the most likely reasons why the vulnerabilities cannot be immediately addressed?

A.

Lack of technical skills, the absence of a test environment, and the absence of an asset inventory

B.

Physical access challenges, the absence of vendor support, and a lack of system documentation

C.

Inaccurate asset inventory, a lack of system documentation, and an absence of authorization

D.

Legacy and proprietary systems, a lack of patch availability, and vendor dependencies

Which of the following best explains the purpose of the Pyramid of Pain in threat intelligence?

A.

To show that changing to different types of indicators and behaviors is difficult for an adversary

B.

To measure how much operational damage a threat actor can cause before detection occurs

C.

To compare open-source intelligence (OSINT) with closed-source intelligence based on collection cost

D.

To organize attack activity into categories such as spoofing, tampering, and repudiation

Which of the following occurs during the analysis phase of the incident response process?

A.

Triage

B.

Alert writing

C.

Reimaging

D.

Isolation

Multiple users report unexpected mouse movements and terminal windows opening.

An analyst reviewing the network traffic logs observes the following:
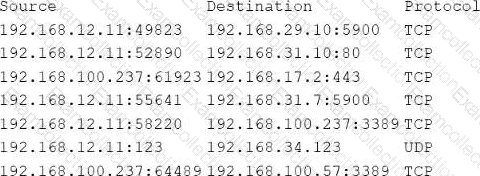
Which of the following is the most likely reason for the reported symptoms?

A.

Activity is on an internally addressable network.

B.

A reverse tunnel is being used to send commands.

C.

Remote Desktop Protocol (RDP) is being used to remotely control the impacted computers.

D.

Virtual Network Computing is being used to connect to systems.

A vulnerability analyst must perform a security assessment on an edge device running various services.

The analyst runs an Nmap port scan and sees the following output:
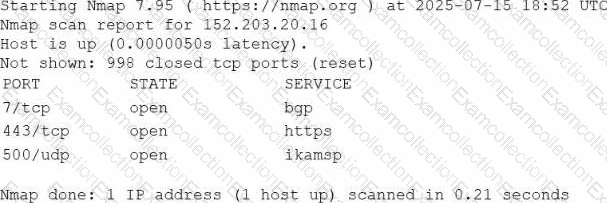
Which of the following should the analyst do next to validate the discovered remote access service is secure?

A.

Verify that the web server certificate is added to certificate store.

B.

Verify that the Border Gateway Protocol (BGP) route has been published.

C.

Verify that the virtual private network (VPN) service is utilizing Main Mode.

D.

Verify that the web server can be pinged.

A Chief Information Security Officer (CISO) is notified of an ongoing incident.

Which of the following explains why the CISO instructs the Chief Executive Officer not to discuss the incident over email?

A.

The security team discovered a vulnerability in the Short Message Service email gateway.

B.

The email system may be compromised.

C.

Emails are not encrypted in transit.

D.

The CISO has not notified the public relations team of the incident.

A vulnerability scanner shows discrepancies between the number of Internet Protocol (IP) addresses across the sites being scanned and the number of systems reporting into the patching system.

Which of the following actions will resolve this issue?

A.

Enable verbose logging in the scanner and check for failures.

B.

Rebuild the vulnerability report selection criteria to account for all sites.

C.

Request the infrastructure team rerun patching deployments.

D.

Conduct a comprehensive asset inventory with the infrastructure team.

An analyst prepares an after action report following an incident in which multiple systems were compromised over several days.

The analyst provides raw event logs from each compromised system in the report and determines that a patient-zero system cannot be found.

Which of the following should the analyst do to determine the patient-zero system?

A.

Establish an accurate timeline of events.

B.

Enable monitoring on the compromised systems.

C.

Isolate the compromised systems before remediation.

D.

Improve the content for incident updates during shift handoff.

E.

Perform a reverse composition analysis on malware packages.

Despite removing malware from some of the affected hosts, several of an organization's internal resources are still unavailable two weeks after the discovery of a major incident.

Which of the following best describes this phase?

A.

Eradication

B.

Post-incident

C.

Detection

D.

Analysis

E.

Preparation