Black Friday Rush: 75% Off All Exam Bundles! Apply the coupon code below before the offer expires! - Ends in 0d 00h 00m 00s - Coupon code: newyear

CyberArk GUARD - CyberArk Guardian Exam

Page: 1 / 2
Total 60 questions

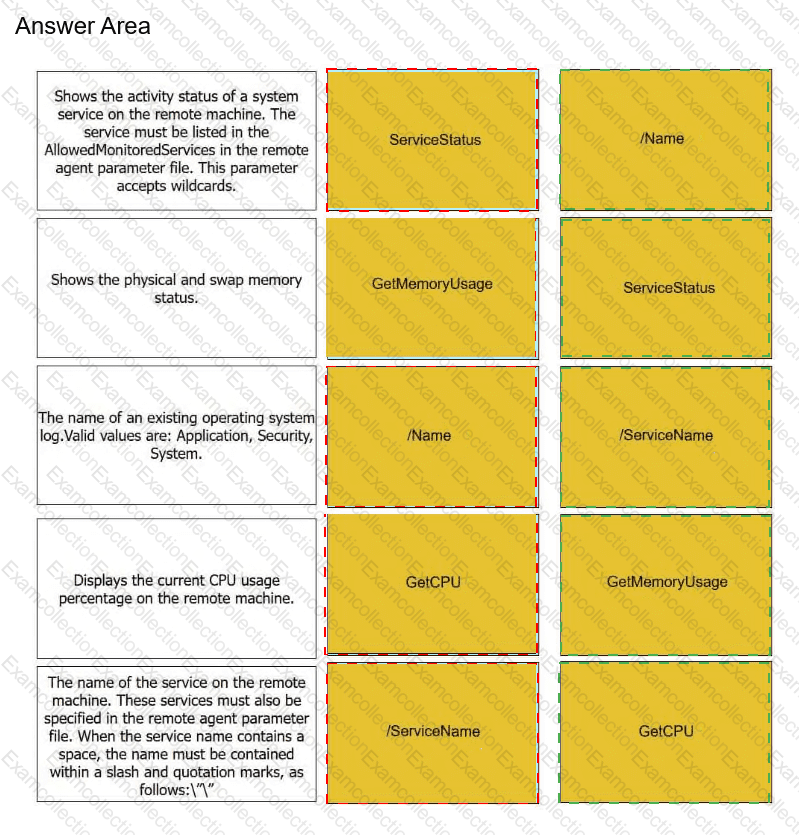
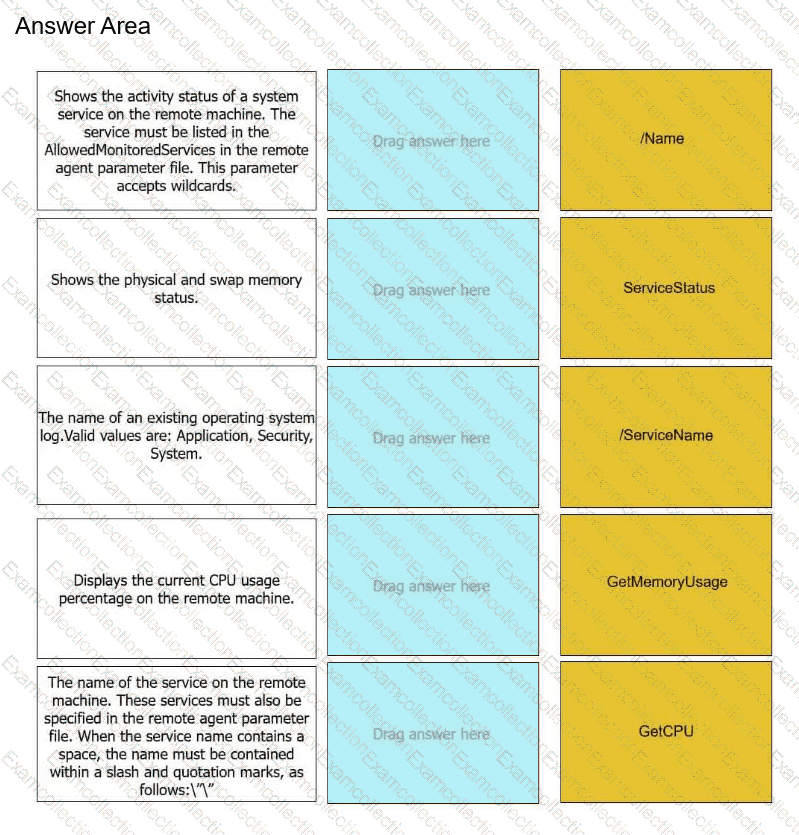
Remote Monitoring lets you receive various information from the EPV and the DR Vault on a remote machine.

Match each parameter to its description:
At which stage is it appropriate to incorporate the C3 Alliance integrations?

A.

Since we already have integrations available and little development is required, they should all be completed in Stage 1.

B.

Integrate the security tools in Stage 1 and other tools such as RPA in Stage 2.

C.

They are less of a risk, so we should leave them until Stage 3 and focus on other privileged accounts first.

D.

They should all be integrated prior to the actual ’go-live' of CyberArk PAM.

How can a single platform manage passwords for multiple Unix flavors?

A.

The Policies and Prompts files can be customized to handle different workflows for different Unix flavors.

B.

You are not able to have more than one unix system type in a single platform.

C.

You can change the platform settings to set up different Unix change commands through the Additional Policies section.

D.

An account can be set up with an additional fields which includes the change and reconcile commands required.

During phase 1 of the CyberArk Blueprint, what action is recommended for managing service accounts?

A.

Create new accounts specifically for the services and then swap them over.

B.

Identify and remove unnecessary privilege's in AD or in local account.

C.

Onboard the account to CyberArk and identify all usages, start rotation.

D.

Create a safe design to onboard the Service accounts to and create platforms for usages.

The enterprise-scale client has a large team of 10 Vault administrators. In accordance with the principle of least privilege, you have advised the client to create separate local CyberArk accounts for managing CyberArk. You created an account named VaultAdmin for activities such as deploying a new platform, and SafeAdmin solely for creating and managing safes. You will then add SafeAdmin to all target-account safes.

You then grant access to the VaultAdmin account to 5 Vault administrators, and grant the other 5 Vault administrators access only to the SafeAdmin account.

The primary benefit of this is:

A.

To follow the principle of Least Privilege.

B.

To follow the principle of separation of duties.

C.

To follow the principles of both least privilege and separation of duties.

D.

'SafeAdmin' now has full access to view the passwords stored in all of the safes, removing this access that is generally granted natively to the 'VaultAdmin' team.

What should be the focus of Stage 1 of the CyberArk Blueprint?

A.

Primarily identities, accounts and systems that have the ability to control an entire environment, both in the cloud or on-prem.

B.

Universal technology platforms such as *NIX and Windows local accounts.

C.

High Risk/High Reward value use cases that are most critical to the operation of the business.

D.

Building integrations to CyberArk PAM such as automation, onboarding and dual control workflows.

A customer has a large deployment that comprises 4 VAULTs, 6 PVWAs, 5 CPMs, and 6 PSMs. The support team has asked you to submit logs and configuration files for each component.

How would you obtain the files in the most efficient way?

A.

Use PAS Reporter to gather the logs and configuration files. Upload the PAS reporter database to the support ticket.

B.

Use CyberArk xRay.

C.

Use CyberArk zBang.

D.

Gather the logs and configuration files from each server manually.

ClientABC is building a PSM farm with 2 servers. They plan to use a physical load balancer configured for least connections.

What else is required as part of this configuration?

A.

Deploy the PSM Healthcheck integration on 1 of the 2 PSM servers. This acts as a centralized healthcheck for both servers.

B.

Deploy the PSM Healthcheck integration on both of the 2 PSM servers. Ensure the load balancer uses this URL.

C.

This is not a supported configuration, PSM only supports round robin load balancing.

D.

Deploy the PSM Healthcheck, however without the load balancer, CyberArk is able to load balance the PSMs internally.

Alice is granted ownership of a Safe both through group membership and through her user ID.

With the default configuration, how does the Vault apply her Safe authorizations?

A.

The Vault applies the combination of Alice's userID-defined and group-defined authorizations.

B.

The Vault applies Alice's group-defined authorizations.

C.

The Vault applies Alice's userID-defined authorizations.

D.

The Vault denies access to Alice.

You deployed your Primary Vault on a CyberArk-supported cloud platform by using a CyberArk-provided image, and deployed a DR Vault in a privately owned data center.

What is the best method for securing the Server Key on the DR Vault?

A.

Use KMS.

B.

Use HSM.

C.

Mount Operator CD every time Vault is started.

D.

Use Azure Key Vault.