Fortinet NSE6_FSM_AN-7.4 - Fortinet NSE 6 - FortiSIEM 7.4 Analyst
Refer to the exhibit.
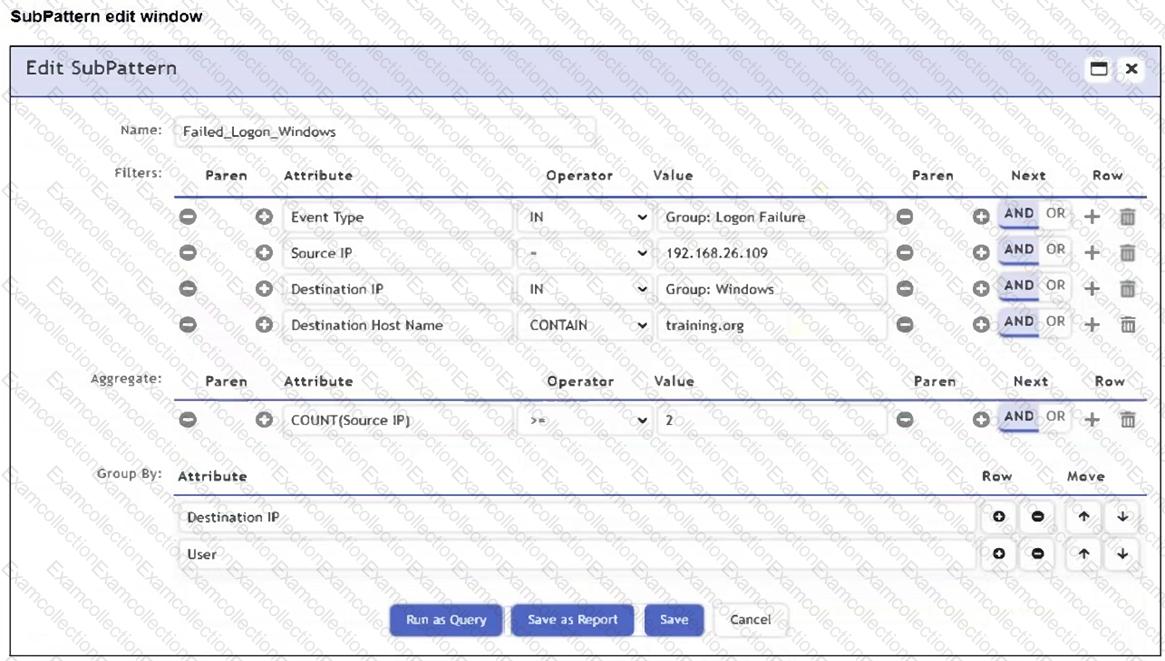
An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.
What is wrong with the rule conditions?
When configuring anomaly detection machine learning, in which step must you select the fields to analyze?
What can you use to send data to FortiSIEM for user and entity behavior analytics (UEBA)?
Which statement about thresholds is true?
Refer to the exhibit.
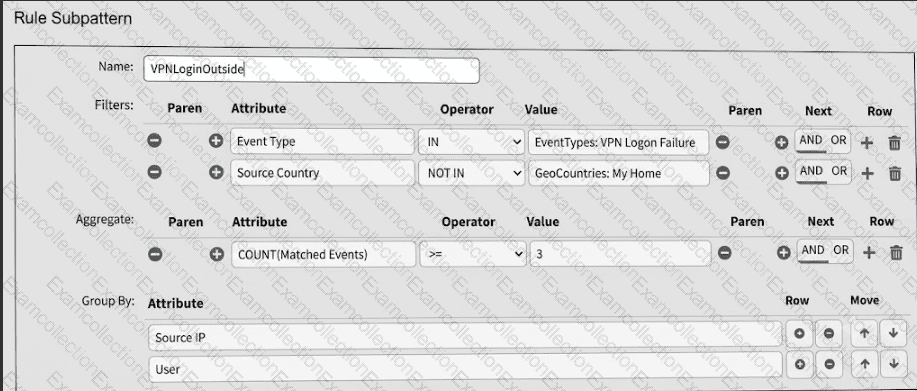
What is this rule attempting to match? (Choose one answer)
Refer to the exhibit.
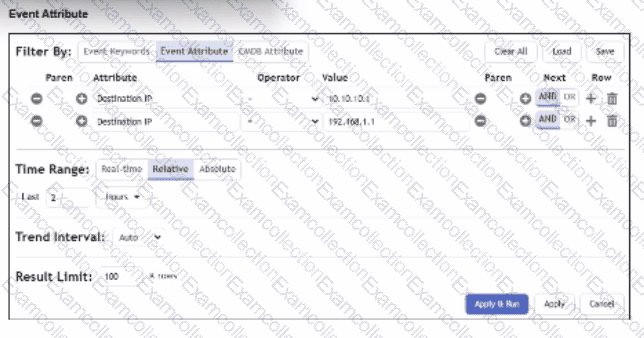
A FortiSIEM analyst is investigating an issue by examining events to two destination IP addresses. However, the analyst is not getting any results from the search.
Based on the selected filter shown in the exhibit, why is the search returning no results?
Refer to the exhibit.
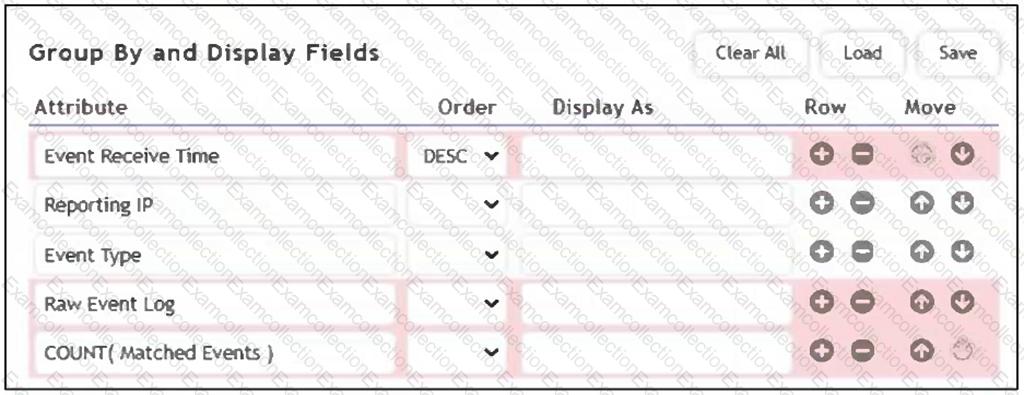
As shown in the exhibit, why are some of the fields highlighted in red?
Refer to the exhibit.
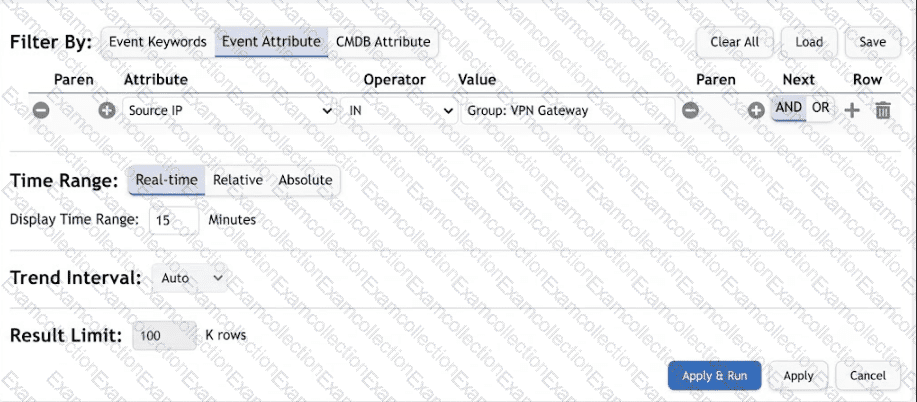
What is the Group: VPN Gateway value a reference to? (Choose one answer)
Refer to the exhibit.
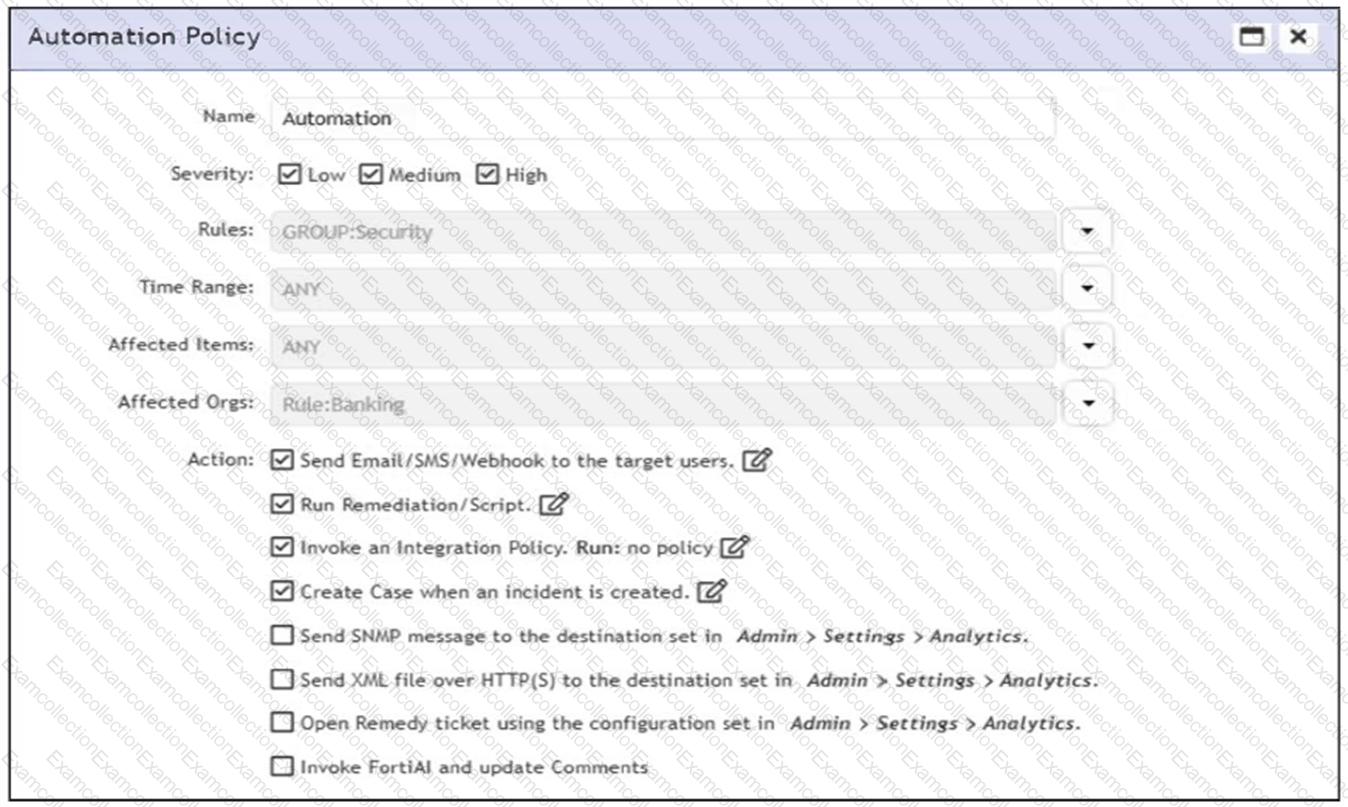
According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?
Which information can FortiSIEM retrieve from FortiClient EMS through an API connection?