


WatchGuard Network-Security-Essentials - Network Security Essentials for Locally-Managed Fireboxes
Total 60 questions
What type of NAT enables clients on a private network to connect to servers on the Internet? (Select one.)
When you migrate a configuration file from one Firebox to a new Firebox, which settings transfer to the new device? (Select two.)
You configured email notifications in WatchGuard Cloud for your Firebox Device Alarms and want to receive an email when your users download any .exe files through an HTTP proxy. You must enable what type of log message in the Firebox configuration? (Select one.)
Your users have no network connectivity on their computers in the 10.0.40.0/24 network. You investigate and discover the DHCP address pool for this network is exhausted, but there are no available IP addresses in the network to assign. Which of these options can you use to expand the IP address space of this network? (Select two.)
When you configure a Branch Office VPN tunnel to a third-party device, AES-GCM encryption is recommended for:
You configured your Firebox as a DHCP server and want to verify the status of the leased addresses. You found this information in Firebox System Manager > Status Report. What is true about DHCP leases in this deployment? (Select two.)
DHCP Leases Log Extract:
lease 10.20.1.100 {
interface vlan20;
starts 4 2023/03/09 21:42:25;
ends 4 2023/03/09 22:42:25;
binding state active;
hardware ethernet 00:50:56:9a:75:d0;
client-hostname "Laptop1";
}
Summary for 10.20.1.0/24: 1 out of 51 IPs are leased
lease 10.0.1.2 {
interface eth1;
starts 4 2023/03/09 21:42:33;
ends 5 2023/03/10 05:42:33;
binding state active;
hardware ethernet 00:50:56:b6:22:9f;
client-hostname "Server1";
}
Summary for 10.0.1.0/24: 1 out of 253 IPs are leased
Summary for all: 2 out of 304 IPs are leased
There is an Internet outage at your primary ISP, but the Internet connection from the Firebox has not failed over to your backup ISP. Both ISP connectors are correctly cabled and have active physical links. What could cause this problem? (Select two.)
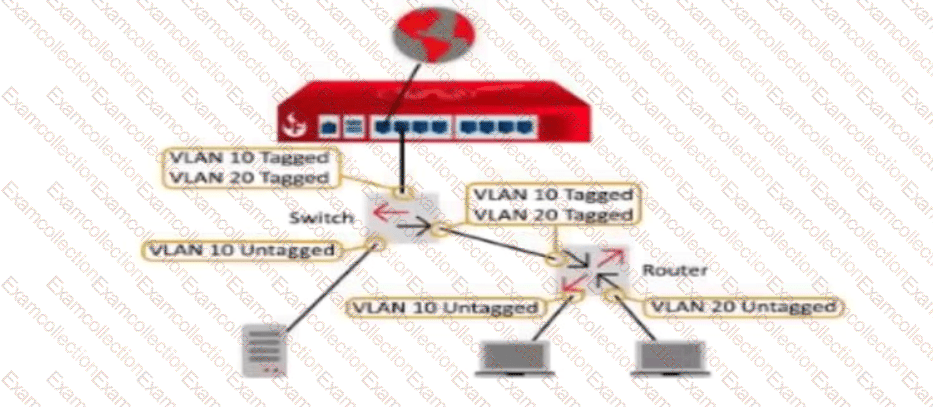
You have an existing network infrastructure built out that uses tagged and untagged VLAN networks. Based on the diagram below, which VLANs must you add to the Firebox interface? (Select one.)
You have five public IP addresses available from your ISP. When you create a Static NAT action, you want to specify one of the public IP addresses for inbound traffic but do not see it in the IP address drop-down list. How can you change the Firebox configuration to see additional public IP addresses in the Static NAT action? (Select one.)
You bought a new Firebox and want to use the configuration from an existing Firebox you already configured. The best way to migrate the configuration is to restore a backup image from the existing Firebox to the new Firebox, then add the new feature key.
