Microsoft SC-100 - Microsoft Cybersecurity Architect
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains 50 virtual machines. Each virtual machine runs different applications on Windows Server 2019.
You need to recommend a solution to ensure that only authorized applications can run on the virtual machines. If an unauthorized application attempts to run or be installed, the application must be blocked automatically until an administrator authorizes the application.
Which security control should you recommend?
You have a Microsoft 365 subscription that uses Microsoft Purview.
You need to recommend a solution that will provide guidance on how to ensure that Personally Identifiable Information (PII) in the subscription adheres to local privacy regulations. The solution must minimize administrative effort.
Which Microsoft Purview solution should you include in the recommendation?
You have a Microsoft Entra tenant. The tenant contains 500 Windows devices that have the Global Secure Access client deployed.
You have a third-party software as a service (SaaS) app named App1.
You plan to implement Global Secure Access to manage access to App1.
You need to recommend a solution to manage connections to App1. The solution must ensure that users authenticate by using their Microsoft Entra credentials before they can connect to App1.
What should you include the recommendation?
You have an Azure subscription named Sub1 that is linked to a Microsoft Entra tenant named contoso.com. Sub1 contains 20 virtual networks named Sub1_VNet1 through Sub1_VNet20.
You have an Azure subscription named Sub2 that is linked to a Microsoft Entra tenant named fabrikam.com. Sub2 contains 20 virtual networks named Sub2_VNet1 through Sub2_VNet20.
You need to deploy an Azure Virtual Network Manager solution that meets the following requirements:
• Blocks SSH traffic on Sub1_VNet20 and Sub2_VNet20 by using network security groups (NSGs)
• Blocks SSH traffic on Sub1_VNet1 through Sub1_VNet19 and Sub2_VNet1 through Sub2_VNet19
• Allows SSH traffic on Sub1_VNet20 and Sub2_VNet20
• Blocks FTP traffic on all the virtual networks
• Minimizes administrative effort
What is minimum number of components required for the deployment?
You have a Microsoft 365 subscription that contains a group named Group!. The subscription is linked to a Microsoft Entra ID P1 tenant.
You have an external software as a service (SaaS) application named Appl. App1 is managed by using a web-based admin portal and supports the use of Microsoft Entra credentials.
You need to ensure that only the members of Group1 who sign in from Microsoft Entra joined devices can access the admin portal of App1
What should you create first in Microsoft Entra?
Your company is moving a big data solution to Azure.
The company plans to use the following storage workloads:
• Azure Storage blob containers
• Azure Data Lake Storage Gen2
• Azure Storage file shares
• Azure Disk Storage
Which two storage workloads support authentication by using Azure Active Directory (Azure AD)?
Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
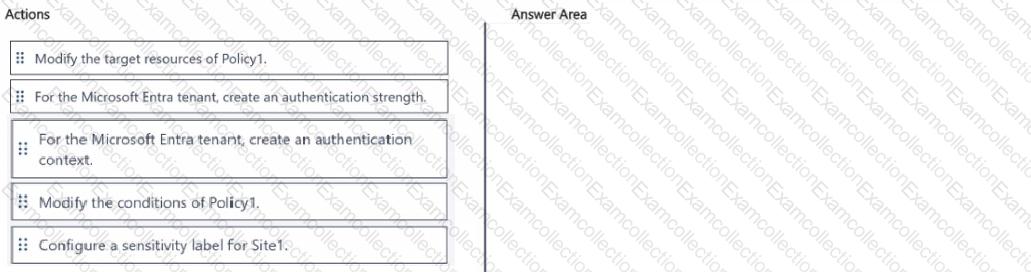
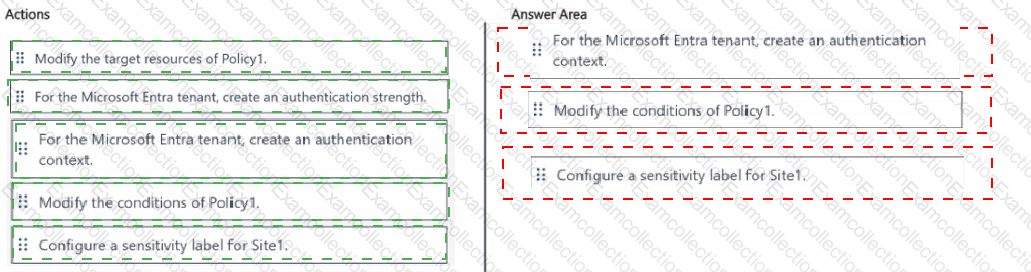
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1.
You have a Conditional Access policy named Policy1 that only allows workload identities from trusted locations to access SharePoint Online.
You plan to move all business-sensitive information to Site1.
You need to ensure that Policy1 applies to Site1 only.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
NOTE: More than one order of answer choices is correct. You will receive credit for any of the correct orders you select.
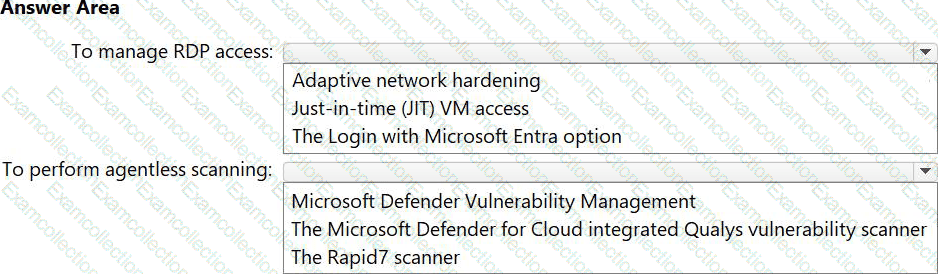
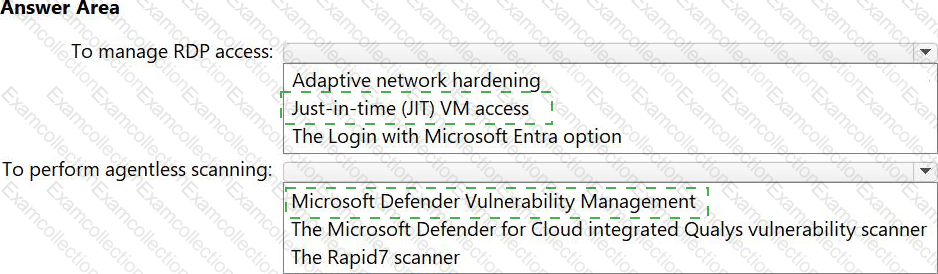
You have an Azure subscription. The subscription contains an Azure Bastion host and 100 virtual machines that run Windows Server 2022. The virtual machines have Microsoft Defender for Servers Plan 2 enabled.
You need to recommend a security solution for the virtual machines that meets the following requirements:
• Administrators must request RDP access to the virtual machines by using the Azure portal.
• Remote Desktop sessions must be limited to a maximum of three hours.
• Agentless scanning must be scheduled to run on each virtual machine.
What should you recommend using? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have a multi-cloud environment that contains an Azure subscription and an Amazon Web Services (AWS) account.
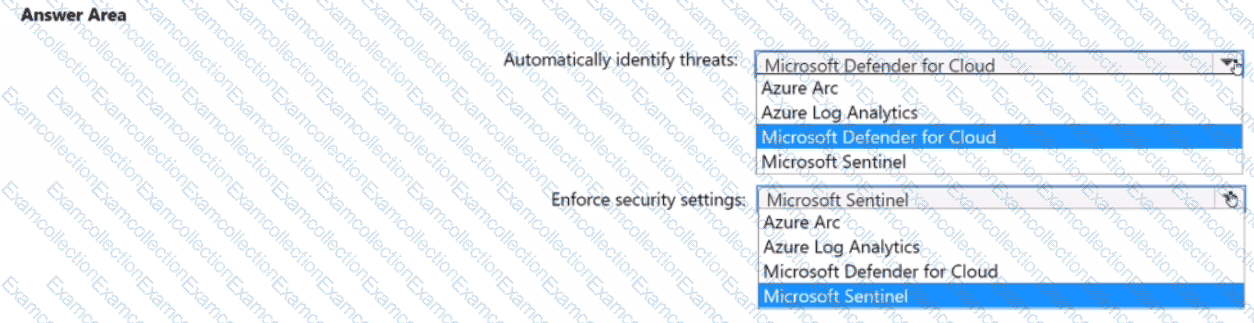
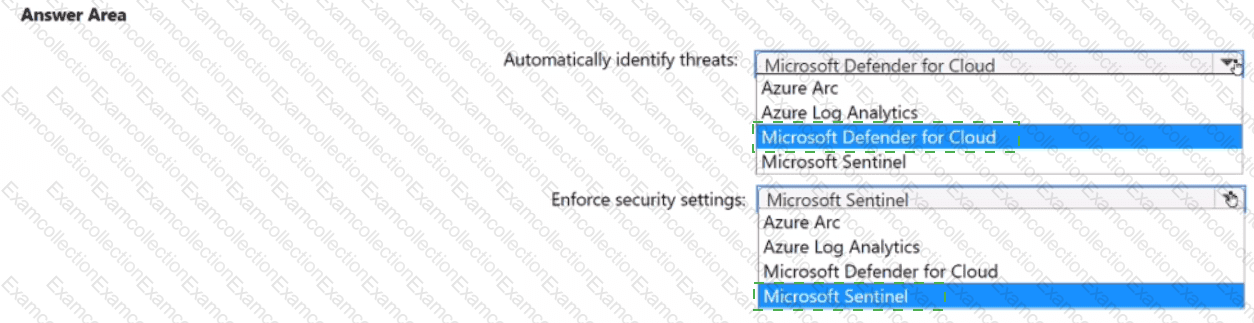
You need to implement security services in Azure to manage the resources in both subscriptions. The solution must meet the following requirements:
• Automatically identify threats found in AWS CloudTrail events.
• Enforce security settings on AWS virtual machines by using Azure policies.
What should you include in the solution for each requirement? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
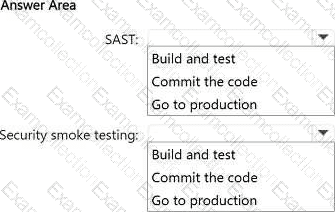
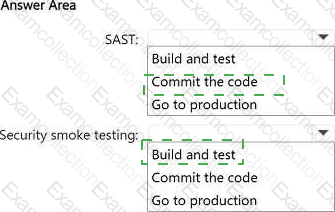
You have an Azure subscription that contains multiple apps. The apps are deployed by using continuous integration and continuous delivery (CI/CD) pipelines in Azure DevOps.
You need to integrate static application security testing (SAST) and security smoke testing into the pipelines based on Microsoft Cloud Adoption Framework for Azure principles.
At which stage of the CI/CID process should each type of test be integrated? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.