


Microsoft SC-100 - Microsoft Cybersecurity Architect
Your company plans to deploy several Azure App Service web apps. The web apps will be deployed to the West Europe Azure region. The web apps will be accessed only by customers in Europe and the United States.
You need to recommend a solution to prevent malicious bots from scanning the web apps for vulnerabilities. The solution must minimize the attach surface.
What should you include in the recommendation?
You have an Azure subscription that contains App Service web apps in four Azure regions. Users connect to the apps from the internet.
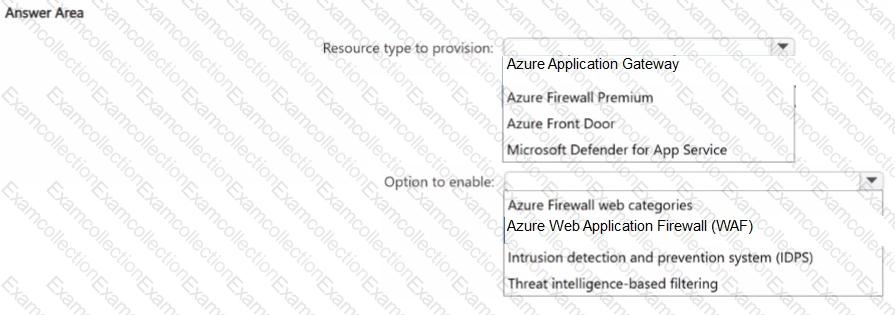
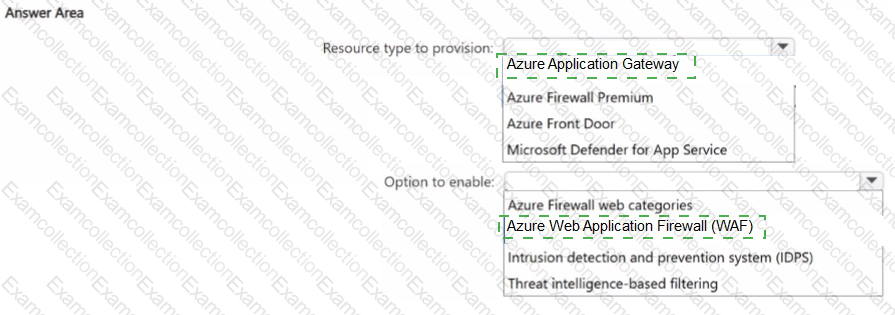
You plan to block requests to the apps if the requests contain security threats specified in the Core Rule Set (CRS) of the Open Web Application Security Project (OWASP).
You need to design a solution to block the requests. The solution must meet the following requirements:
• Maintain access to the apps in the event of a region outage.
• Minimize the number of resources required.
What should you include in the design? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription.
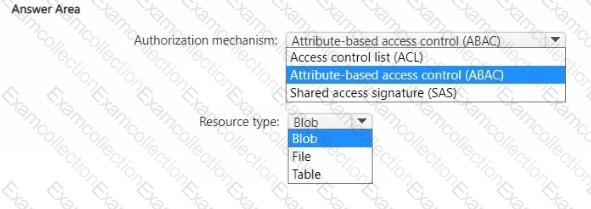
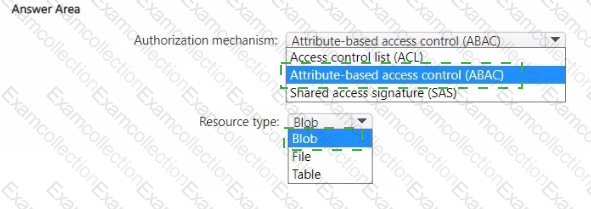
You plan to deploy a storage account named storage1 that will store confidential data. You will assign tags to the confidential data.
You need to ensure that access to storage1 can be defined by using the assigned tags.
Which authorization mechanism should you enable, and which type of resource should you use to store the data? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company plans to evaluate the security of its Azure environment based on the principles of the Microsoft Cloud Adoption Framework for Azure.
You need to recommend a cloud-based service to evaluate whether the Azure resources comply with the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF).
What should you recommend?
