CompTIA SY0-701 - CompTIA Security+ Exam 2026
An administrator is estimating the cost associated with an attack that could result in the replacement of a physical server. Which of the following processes is the administrator performing?
A vendor needs to remotely and securely transfer files from one server to another using the command line. Which of the following protocols should be Implemented to allow for this type of access? (Select two).
During a recent company safety stand-down, the cyber-awareness team gave a presentation on the importance of cyber hygiene. One topic the team covered was best practices for printing centers. Which of the following describes an attack method that relates to printing centers?
A systems administrator needs to ensure the secure communication of sensitive data within the organization ' s private cloud. Which of the following is the best choice for the administrator to implement?
Sine© a recent upgrade (o a WLAN infrastructure, several mobile users have been unable to access the internet from the lobby. The networking team performs a heat map survey of the building and finds several WAPs in the area. The WAPs are using similar frequencies with high power settings. Which of the following installation considerations should the security team evaluate next?
Which of the following actions would reduce the number of false positives for an analyst to manually review?
The security operations center is researching an event concerning a suspicious IP address A security analyst looks at the following event logs and discovers that a significant portion of the user accounts have experienced faded log-In attempts when authenticating from the same IP address:
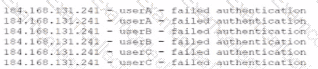
Which of the following most likely describes attack that took place?
Which of the following security concepts is the best reason for permissions on a human resources fileshare to follow the principle of least privilege?
Which of the following is the best way to provide secure remote access for employees while minimizing the exposure of a company ' s internal network?
A company wants to protect a specialized legacy platform that controls the physical flow of gas inside of pipes. Which of the following environments does the company need to secure to best achieve this goal?
Which of the following definitions best describes the concept of log co-relation?
Which of the following vulnerabilities is associated with installing software outside of a manufacturer’s approved software repository?
Which of the following would most likely prevent exploitation of an end-of-life, business-critical system?
Which of the following will most likely lead an organization to revise its change management policy?
A company ' s accounting department receives an urgent payment message from the company ' s bank domain with instructions to wire transfer funds. The sender requests that the transfer be completed as soon as possible. Which of the following attacks is described?
Which of the following best represents an application that does not have an on-premises requirement and is accessible from anywhere?
Which of the following vulnerabilities will lead to a successful attack that injects < IMG src= ' http://attackersite.net/mycode.sh ' > into a web application?
Which of the following is the most appropriate reason for a server technician to disable unused ports and services on an externally facing DNS server?
After reviewing the following vulnerability scanning report:
Server:192.168.14.6
Service: Telnet
Port: 23 Protocol: TCP
Status: Open Severity: High
Vulnerability: Use of an insecure network protocol
A security analyst performs the following test:
nmap -p 23 192.168.14.6 —script telnet-encryption
PORT STATE SERVICE REASON
23/tcp open telnet syn-ack
I telnet encryption:
| _ Telnet server supports encryption
Which of the following would the security analyst conclude for this reported vulnerability?
A company’s legal department drafted sensitive documents in a SaaS application and wants to ensure the documents cannot be accessed by individuals in high-risk countries. Which of the following is the most effective way to limit this access?