CompTIA SY0-701 - CompTIA Security+ Exam 2026
An organization is evaluating the cost of licensing a new solution to prevent ransomware. Which of the following is the most helpful in making this decision?
Which of the following should a security team do first before a new web server goes live?
Which of the following would most likely be used by attackers to perform credential harvesting?
Which of the following control types is AUP an example of?
A technician wants to improve the situational and environmental awareness of existing users as they transition from remote to in-office work. Which of the following is the best option?
A security analyst finds a rogue device during a monthly audit of current endpoint assets that are connected to the network. The corporate network utilizes 002.1X for access control. To be allowed on the network, a device must have a Known hardware address, and a valid user name and password must be entered in a captive portal. The following is the audit report:
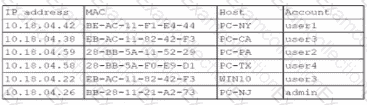
Which of the following is the most likely way a rogue device was allowed to connect?
Which of the following should an internal auditor check for first when conducting an audit of the organization’s risk management program?
An administrator learns that users are receiving large quantities of unsolicited messages. The administrator checks the content filter and sees hundreds of messages sent to multiple users. Which of the following best describes this kind of attack?
A company is using a legacy FTP server to transfer financial data to a third party. The legacy system does not support SFTP, so a compensating control is needed to protect the sensitive, financial data in transit. Which of the following would be the most appropriate for the company to use?
An organization has learned that its data is being exchanged on the dark web. The CIO
has requested that you investigate and implement the most secure solution to protect employee accounts.
INSTRUCTIONS
Review the data to identify weak security practices and provide the most appropriate
security solution to meet the CIO ' s requirements.
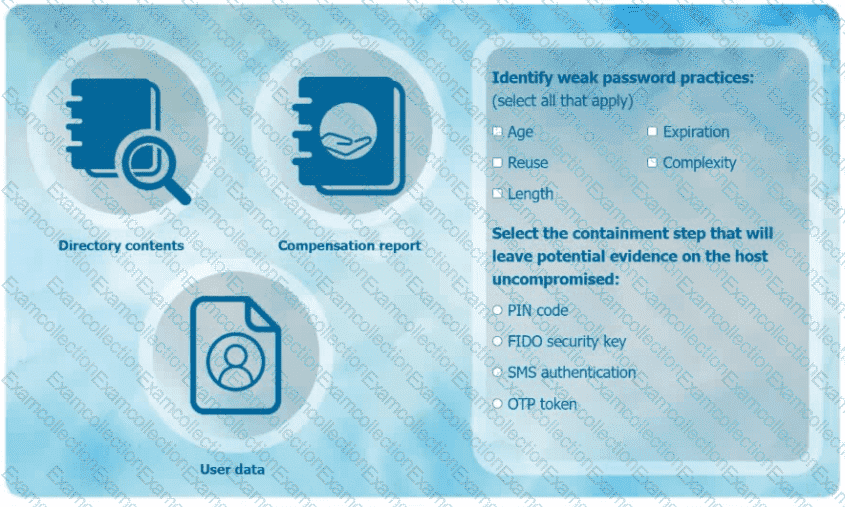
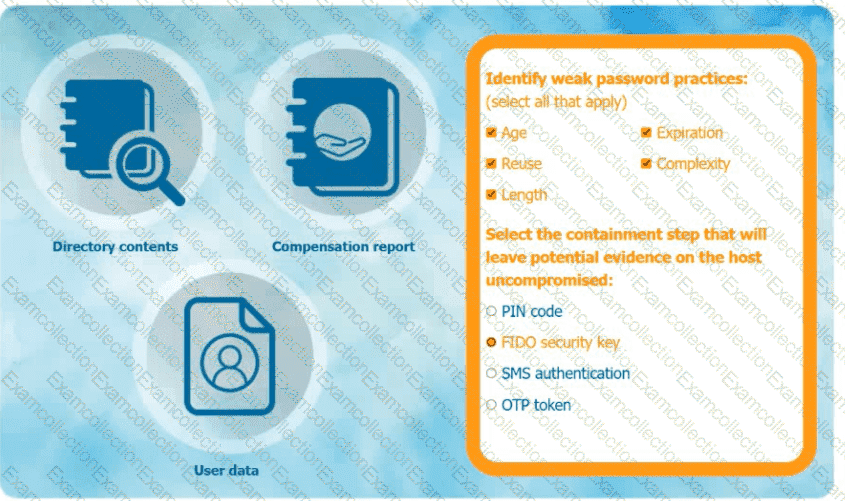 A screenshot of a computer AI-generated content may be incorrect.
Which of the following describes the reason root cause analysis should be conducted as part of incident response?
Which of the following would be the best way to test resiliency in the event of a primary power failure?
Which of the following is most important to maintain when it comes to evidence during a digital forensic investigation?
After a recent ransomware attack on a company ' s system, an administrator reviewed the log files. Which of the following control types did the administrator use?
Which of the following best summarizes the reason for an AUP?
A customer of a large company receives a phone call from someone claiming to work for the company and asking for the customer ' s credit card information. The customer sees the caller ID is the same as the company ' s main phone number. Which of the following attacks is the customer most likely a target of?
A company purchased cyber insurance to address items listed on the risk register. Which of the following strategies does this represent?
A newly appointed board member with cybersecurity knowledge wants the board of directors to receive a quarterly report detailing the number of incidents that impacted the organization. The systems administrator is creating a way to present the data to the board of directors. Which of the following should the systems administrator use?
A malicious insider from the marketing team alters records and transfers company funds to a personal account. Which of the following methods would be the best way to secure company records in the future?
A security administrator is implementing encryption on all hard drives in an organization. Which of the following security concepts is the administrator applying?