CompTIA SY0-701 - CompTIA Security+ Exam 2026
Several employees received a fraudulent text message from someone claiming to be the Chief Executive Officer (CEO). The message stated:
“I’m in an airport right now with no access to email. I need you to buy gift cards for employee recognition awards. Please send the gift cards to following email address.â€
Which of the following are the best responses to this situation? (Choose two).
An employee from the accounting department logs in to the website used for processing the company ' s payments. After logging in, a new desktop application automatically downloads on the employee ' s computer and causes the computer to restart. Which of the following attacks has occurred?
An organization discovers that its cold site does not have enough storage and computers available. Which of the following was most likely the cause of this failure?
A network administrator wants to ensure that network traffic is highly secure while in transit. Which of the following actions best describes the actions the network administrator should take?
An employee who was working remotely lost a mobile device containing company data. Which of the following provides the best solution to prevent future data loss?
Which of the following practices would be best to prevent an insider from introducing malicious code into a company ' s development process?
A Chief Information Security Officer (CISO) has developed information security policies that relate to the software development methodology. Which of the following would the CISO most likely include in the organization ' s documentation?
A site reliability engineer is designing a recovery strategy that requires quick failover to an identical site if the primary facility goes down. Which of the following types of sites should the engineer consider?
A security administrator recently reset local passwords and the following values were recorded in the system:
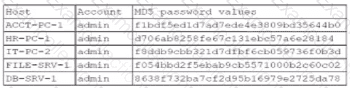
Which of the following in the security administrator most likely protecting against?
While troubleshooting a firewall configuration, a technician determines that a “deny any†policy should be added to the bottom of the ACL. The technician updates the policy, but the new policy causes several company servers to become unreachable.
Which of the following actions would prevent this issue?
Which of the following best describes a method for ongoing vendor monitoring in third-party risk management?
Which of the following is the most likely to be used to document risks, responsible parties, and thresholds?
An organization has a new regulatory requirement to implement corrective controls on a financial system. Which of the following is the most likely reason for the new requirement?
A company needs to determine whether authentication weaknesses in a customer-facing web application exist. Which of the following is the best technique to use?
Which of the following best distinguishes hacktivists from insider threats?
Which of the following would best prepare a security team for a specific incident response scenario?
Which vulnerability is most likely mitigated by setting up an MDM platform?
Which of the following digital forensics activities would a security team perform when responding to legal requests in a pending investigation?
A company ' s online shopping website became unusable shortly after midnight on January 30, 2023. When a security analyst reviewed the database server, the analyst noticed the following code used for backing up data:
Which of the following should the analyst do next?
The marketing department set up its own project management software without telling the appropriate departments. Which of the following describes this scenario?