Black Friday Rush: 75% Off All Exam Bundles! Apply the coupon code below before the offer expires! - Ends in 0d 00h 00m 00s - Coupon code: newyear

Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2

Page: 11 / 14
Total 444 questions

An analyst is investigating a potentially compromised endpoint within the network and pulls a host report for the endpoint in question to collect metrics and documentation. What information should be taken from this report for the investigation?

A.

client applications by user, web applications, and user connections

B.

number of attacked machines, sources of the attack, and traffic patterns

C.

intrusion events, host connections, and user sessions

D.

threat detections over time and application protocols transferring malware

An administrator needs to configure Cisco FMC to send a notification email when a data transfer larger than 10 MB is initiated from an internal host outside of standard business hours. Which Cisco FMC feature must be configured to accomplish this task?

A.

file and malware policy

B.

application detector

C.

intrusion policy

D.

correlation policy

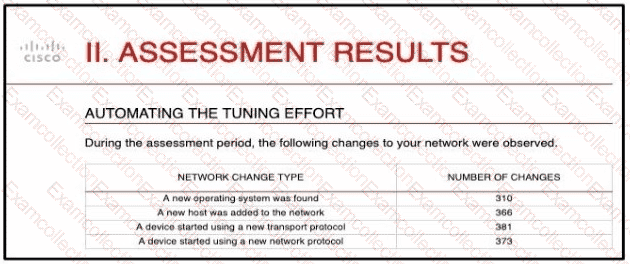
Refer to the exhibit.

And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?

A.

Cisco Firepower automatically updates the policies.

B.

The administrator requests a Remediation Recommendation Report from Cisco Firepower

C.

Cisco Firepower gives recommendations to update the policies.

D.

The administrator manually updates the policies.

An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?

A.

Install the static backup route and modify the metric to be less than the primary route.

B.

Configure EIGRP routing on the FMC to ensure that dynamic routes are always updated.

C.

Use a default route on the FMC instead of having multiple routes contending for priority.

D.

Create the backup route and use route tracking on both routes to a destination IP address in the network.

An engineer must deploy a high-availability pair that includes two Cisco Secure Firewall Threat Defense devices. The deployment must provide a mechanism that protects synchronization traffic between the members. Which action must the engineer take?

A.

Configure an SSL VPN tunnel between the units.

B.

Select the Key Generation method for IPsec encryption.

C.

Encrypt the synchronization traffic with SSL.

D.

Clear the commit queue when synchronization begins.

A network administrator registered a new FTD to an existing FMC. The administrator cannot place the FTD in transparent mode. Which action enables transparent mode?

A.

Add a Bridge Group Interface to the FTD before transparent mode is configured.

B.

Dereglster the FTD device from FMC and configure transparent mode via the CLI.

C.

Obtain an FTD model that supports transparent mode.

D.

Assign an IP address to two physical interfaces.

An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device. When the engineer navigates to URL for Secure Firewall Management Center at:

.. < FMC IP > /capture/CAP/pcap/sample.pcap

An engineer receives a 403: Forbidden error instead of being provided with the PCAP file. Which action resolves the issue?

A.

Disable the HTTPS server and use HTTP.

B.

Enable the proxy setting in the device platform policy.

C.

Enable HTTPS in the device platform policy.

D.

Disable the proxy setting on the client browser.

An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?

A.

Deploy the device in routed mode and allow DHCP traffic in the access control policies.

B.

Deploy the device in routed made aid enable the DHCP Relay feature.

C.

Deploy the device in transparent mode and allow DHCP traffic in the access control policies

D.

Deploy the device in transparent mode and enable the DHCP Server feature.

A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?

A.

The malware license has not been applied to the Cisco FTD.

B.

The Cisco FMC cannot reach the Internet to analyze files.

C.

A file policy has not been applied to the access policy.

D.

Only Spero file analysis is enabled.

A network administrator needs to create a policy on Cisco Firepower to fast-path traffic to avoid Layer 7 inspection. The rate at which traffic is inspected must be optimized. What must be done to achieve this goal?

A.

Enable lhe FXOS for multi-instance.

B.

Configure a prefilter policy.

C.

Configure modular policy framework.

D.

Disable TCP inspection.