Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?
Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?
Refer to the exhibit.
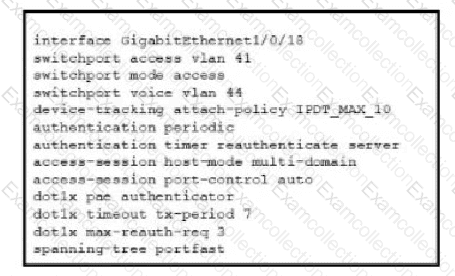
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.
Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?
How does Cisco Stealthwatch Cloud provide security for cloud environments?
An organization configures Cisco Umbrella to be used for its DNS services. The organization must be able to block traffic based on the subnet that the endpoint is on but it sees only the requests from its public IP address instead of each internal IP address. What must be done to resolve this issue?
Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?
What is a difference between a DoS attack and a DDoS attack?
Which Cisco security solution integrates with cloud applications like Dropbox and Office 365 while protecting data from being exfiltrated?
Refer to the exhibit. When creating an access rule for URL filtering, a network engineer adds certain categories and individual URLs to block. What is the result of the configuration?
An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?
A Cisco AMP for Endpoints administrator configures a custom detection policy to add specific MD5 signatures The configuration is created in the simple detection policy section, but it does not work What is the reason for this failure?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
Which metric is used by the monitoring agent to collect and output packet loss and jitter information?
What is a characteristic of a bridge group in ASA Firewall transparent mode?
What is the difference between deceptive phishing and spear phishing?