Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
What is a characteristic of Cisco ASA Netflow v9 Secure Event Logging?
An engineer is configuring a Cisco ESA and wants to control whether to accept or reject email messages to a
recipient address. Which list contains the allowed recipient addresses?
What is the purpose of a NetFlow version 9 template record?
A customer has various external HTTP resources available including Intranet. Extranet, and Internet, with a proxy configuration running in explicit mode Which method allows the client desktop browsers to be configured to select when to connect direct or when to use the proxy?
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
Refer to the exhibit.
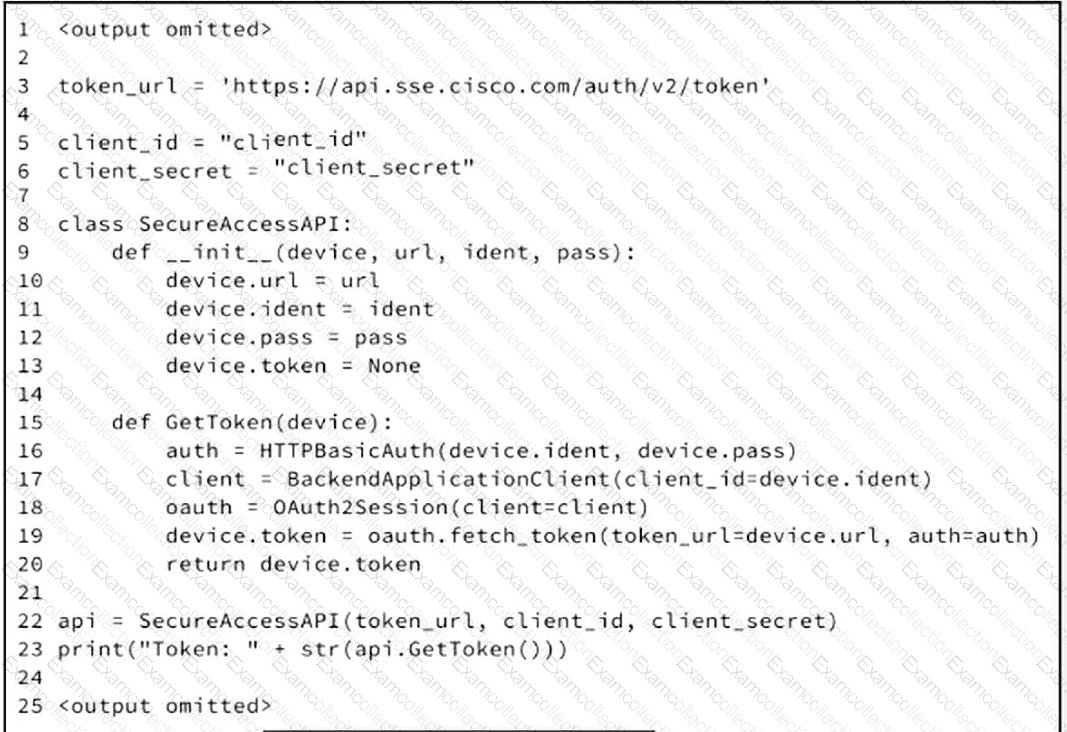
An engineer creates a Python script to make an API call to Cisco Secure Access. Which output should be expected from the script?
Refer to the exhibit.
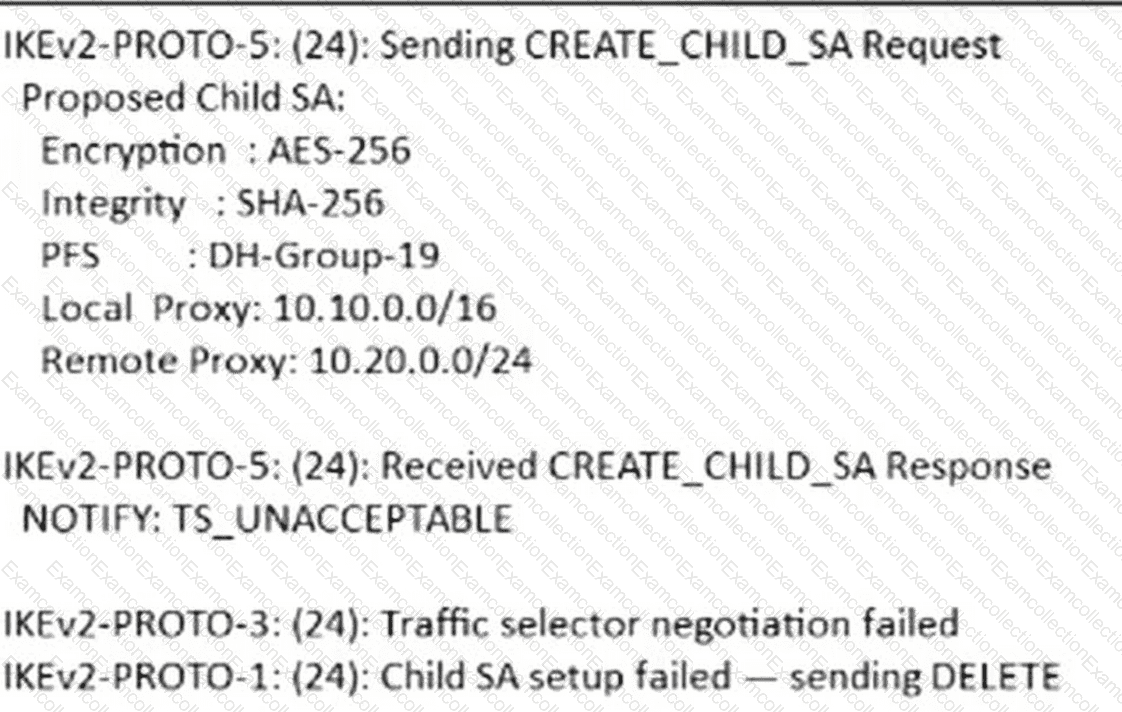
A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_SA. The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?
What does Cisco ISE use to collect endpoint attributes that are used in profiling?
What is the result of the ACME-Router(config)#login block-for 100 attempts 4 within 60 command on a Cisco IOS router?
For which type of attack is multifactor authentication an effective deterrent?
A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?
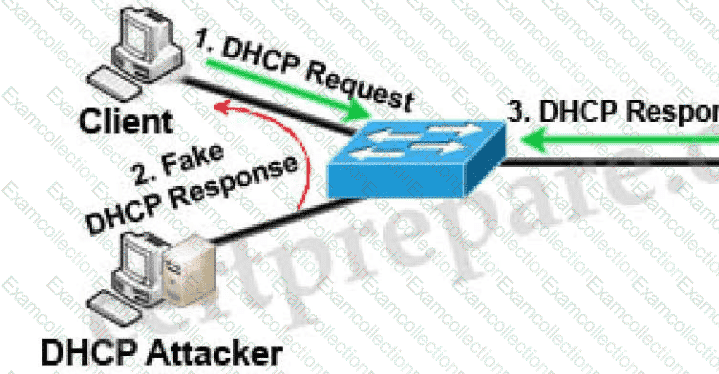
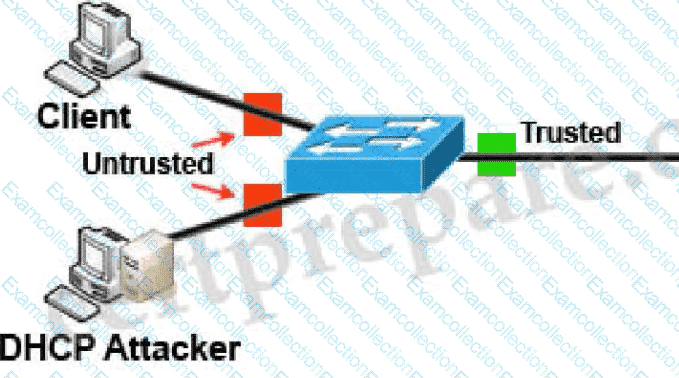
An administrator is configuring a DHCP server to better secure their environment. They need to be able to ratelimit the traffic and ensure that legitimate requests are not dropped. How would this be accomplished?
What is a benefit of using Cisco FMC over Cisco ASDM?
An engineer is configuring 802.1X authentication on Cisco switches in the network and is using CoA as a mechanism. Which port on the firewall must be opened to allow the CoA traffic to traverse the network?
When choosing an algorithm to us, what should be considered about Diffie Hellman and RSA for key
establishment?