Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?
An organization wants to provide visibility and to identify active threats in its network using a VM. The
organization wants to extract metadata from network packet flow while ensuring that payloads are not retained
or transferred outside the network. Which solution meets these requirements?
Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the
deployment?
What are two security benefits of an MDM deployment? (Choose two.)
What is a difference between GRE over IPsec and IPsec with crypto map?
Refer to the exhibit.
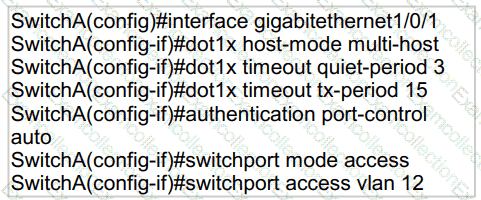
An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?
When a transparent authentication fails on the Web Security Appliance, which type of access does the end user get?
Which two features of Cisco Email Security can protect your organization against email threats? (Choose two)
A large retail enterprise is deploying Cisco Secure Private Access to enable remote employees to reach internal applications without manual intervention. The IT department requires a seamless, zero-touch enrollment process in which users are registered and authenticated transparently without requiring end-user action. The architecture must support robust high availability for back-end connectivity to ensure continuous access to private resources. Which configuration approach must the administrator implement to meet the requirement?
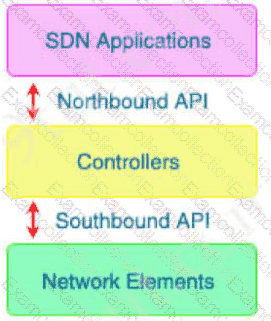
Which type of API is being used when a controller within a software-defined network architecture dynamically
makes configuration changes on switches within the network?
An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?
A financial services firm is concerned about employees inadvertently pasting sensitive customer account information into public generative AI websites. The security team needs to implement a solution that inspects outbound traffic and prevents the transmission of sensitive data to AI platforms. Which two configuration actions must the administrator perform on Cisco Secure Access to achieve the requirement? (Choose two.)
What is the term for when an endpoint is associated to a provisioning WLAN that is shared with guest
access, and the same guest portal is used as the BYOD portal?
An engineer is trying to securely connect to a router and wants to prevent insecure algorithms from being used.
However, the connection is failing. Which action should be taken to accomplish this goal?
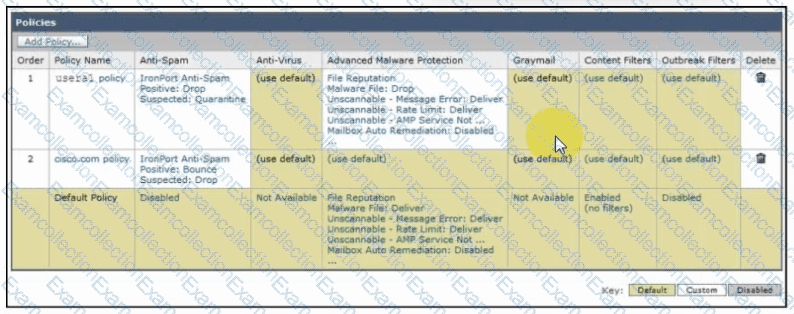
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?