Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmas50

Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Page: 2 / 16
Total 801 questions

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?

A.

Cisco CTA

B.

Cisco Encrypted Traffic Analytics

C.

Cisco Umbrella

D.

Cisco Secure Network Analytics

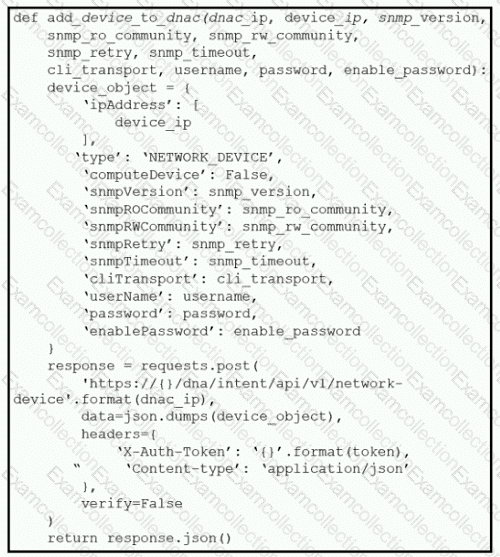
Refer to the exhibit.

What is the result of this Python script of the Cisco DNA Center API?

A.

adds authentication to a switch

B.

adds a switch to Cisco DNA Center

C.

receives information about a switch

D.

deletes a switch from Cisco DNA Center

Which policy does a Cisco Secure Web Appliance use to block or monitor URL requests based on the reputation score?

A.

Encryption

B.

Enforcement Security

C.

Cisco Data Security

D.

Outbound Malware Scanning

A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?

A.

Enable global settings with default URL filtering.

B.

Configure a file policy in an access control policy.

C.

Apply web filtering in an access control policy.

D.

Block the social-media URL category in the destination-network condition of an access control rule.

Which industry standard is used to integrate Cisco ISE and pxGrid to each other and with other

interoperable security platforms?

A.

IEEE

B.

IETF

C.

NIST

D.

ANSI

An engineer must deploy Cisco Secure Email with Cloud URL Analysis and must meet these requirements:

To protect the network from large-scale virus outbreaks

To protect the network from non-viral attacks such as phishing scams and malware distribution

To provide active analysis of the structure of the URL and information about the domain and page contents

Which two prerequisites must the engineer ensure are configured? (Choose two.)
A.

Scanning enabled for each Verdict, Prepend Subject and Deliver.

B.

Outbreak Filters must be enabled globally.

C.

Enable TLS by setting to Preferred to the Default Domain.

D.

Service Logs must be enabled.

E.

Enable Rejected Connection Logging.

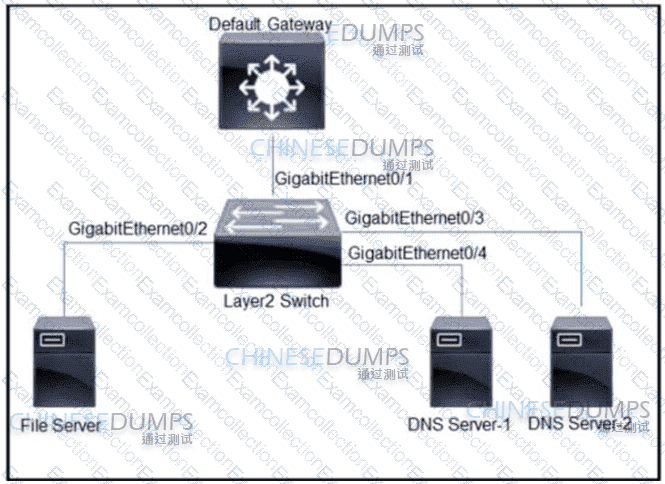
Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?

A.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as isolated port, and GigabitEthernet0/3 and GigabitEthernet0/4 as promiscuous ports.

B.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as promiscuous port, Gigabit Ethernet0/3 and GigabitEthernet0/4 as isolated ports C. Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as isolated port and GigabitEthernet0/3 and GrgabitEthernet0/4 as community ports

C.

Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as community port, and GigabitEthernet0/3 and GrgabitEthernet0/4 as isolated ports.

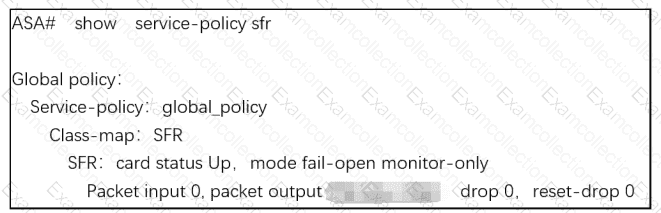
Refer to the exhibit.

What are two indications of the Cisco Firepower Services Module configuration?

(Choose two.)

A.

The module is operating in IDS mode.

B.

Traffic is blocked if the module fails.

C.

The module fails to receive redirected traffic.

D.

The module is operating in IPS mode.

E.

Traffic continues to flow if the module fails.

A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?

A.

denial -of-service

B.

cross-site request forgery

C.

man-in-the-middle

D.

SQL injection

Which capability allows an administrator to configure forensics rules in Cisco Secure Workload?

A.

Custom clauses

B.

MITRE ATT & CK framework only predefined

C.

Cisco Secure Workload predefined

D.

Windows or Linux application

What are two Detection and Analytics Engines of Cognitive Threat Analytics? (Choose two)

A.

data exfiltration

B.

command and control communication

C.

intelligent proxy

D.

snort

E.

URL categorization

What is a difference between DMVPN and sVTI?

A.

DMVPN supports tunnel encryption, whereas sVTI does not.

B.

DMVPN supports dynamic tunnel establishment, whereas sVTI does not.

C.

DMVPN supports static tunnel establishment, whereas sVTI does not.

D.

DMVPN provides interoperability with other vendors, whereas sVTI does not.

Which two Cisco ISE components must be configured for BYOD? (Choose two.)

A.

local WebAuth

B.

central WebAuth

C.

null WebAuth

D.

guest

E.

dual

How does a cloud access security broker function?
A.

It is an authentication broker to enable single sign-on and multi-factor authentication for a cloud solution

B.

lt integrates with other cloud solutions via APIs and monitors and creates incidents based on events from the cloud solution

C.

It acts as a security information and event management solution and receives syslog from other cloud solutions.

D.

It scans other cloud solutions being used within the network and identifies vulnerabilities