Pre-Winter Sale Special Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmas50

Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)

Page: 5 / 16
Total 801 questions

What does Cisco AMP for Endpoints use to help an organization detect different families of malware?

A.

Ethos Engine to perform fuzzy fingerprinting

B.

Tetra Engine to detect malware when me endpoint is connected to the cloud

C.

Clam AV Engine to perform email scanning

D.

Spero Engine with machine learning to perform dynamic analysis

An engineer is configuring their router to send NetfFow data to Stealthwatch which has an IP address of 1 1 11 using the flow record Stea!thwatch406397954 command Which additional command is required to complete the flow record?

A.

transport udp 2055

B.

match ipv4 ttl

C.

cache timeout active 60

D.

destination 1.1.1.1

Refer to the exhibit.

=== Cisco Secure Endpoint - Detection Event ===

Endpoint : LAB-WKSTN-047 User: user1

Policy Group : Lab-Workstations Mode: Audit

Engine : ETHOS (fuzzy fingerprint)

Disposition : Malicious

File : C:\Users\user1\AppData\Local\Temp\svchost32.exe

SHA256 : 3a9f2c1d...e881b4a7

Parent Process: winword.exe

Threat Name : W32.Trojan.GenericKD.Agent

Retrospective : Previously UNKNOWN

Disposition changed to MALICIOUS at 09:31:55 UTC

File Activity : Created, Executed

Network : TCP outbound - > 91.205.188.47:4444

DNS query: c2-update.pharmadomain.ru

Quarantine : NOT quarantined (Audit mode active)

A security analyst at a pharmaceutical company is reviewing a Cisco Secure Endpoint malware-detection alert triggered on a laboratory workstation. The analyst observes the event data above. Which two things are occurring? (Choose two.)

A.

The antivirus engine update interval on workstation LAB-WKSTN-047 is too infrequent.

B.

The endpoint is running in Audit mode; the file was detected but not quarantined.

C.

The endpoint is running in Audit mode; the file was detected and quarantined.

D.

The file executed, was spawned by winword.exe, and opened an outbound connection to external command-and-control infrastructure.

E.

The parent file winword.exe is on a custom application allow list, permitting the malicious file to execute.

A Cisco ISE engineer configures Central Web Authentication (CWA) for wireless guest access and must have the guest endpoints redirect to the guest portal for authentication and authorization. While testing the policy, the engineer notices that the device is not redirected and instead gets full guest access. What must be done for the redirect to work?

A.

Tag the guest portal in the CWA part of the Common Tasks section of the authorization profile for the authorization policy line that the unauthenticated devices hit.

B.

Use the track movement option within the authorization profile for the authorization policy line that the unauthenticated devices hit.

C.

Create an advanced attribute setting of Cisco:cisco-gateway-id=guest within the authorization profile for the authorization policy line that the unauthenticated devices hit.

D.

Add the DACL name for the Airespace ACL configured on the WLC in the Common Tasks section of the authorization profile for the authorization policy line that the unauthenticated devices hit.

Which exfiltration method does an attacker use to hide and encode data inside DNS requests and queries?

A.

DNS tunneling

B.

DNSCrypt

C.

DNS security

D.

DNSSEC

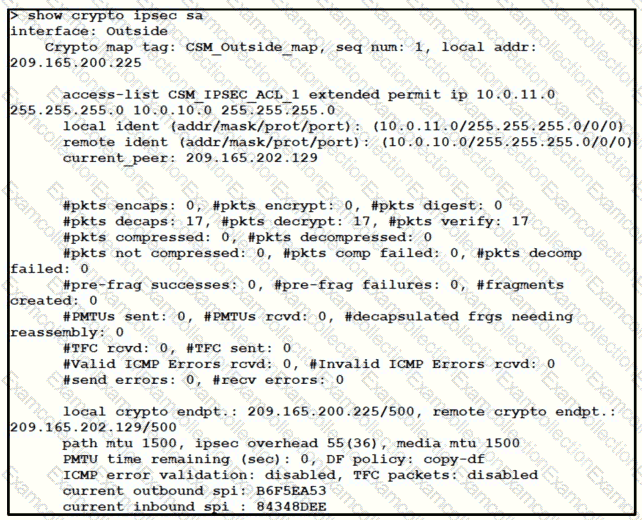
Refer to the exhibit.

Traffic is not passing through IPsec site-to-site VPN on the Firepower Threat Defense appliance. What is causing this issue?
A.

No split-tunnel policy is defined on the Firepower Threat Defense appliance.

B.

The access control policy is not allowing VPN traffic in.

C.

Site-to-site VPN peers are using different encryption algorithms.

D.

Site-to-site VPN preshared keys are mismatched.

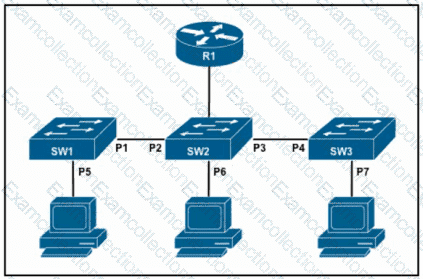
Refer to the exhibit. The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

A.

P2 and P3 only

B.

P2, P3, and P6 only

C.

P5, P6, and P7 only

D.

P1, P2, P3, and P4 only

A web hosting company must upgrade its older, unsupported on-premises servers. The company wants a cloud solution in which the cloud provider is responsible for:

Server patching

Application maintenance

Data center security

Disaster recovery

Which type of cloud meets the requirements?

A.

Hybrid

B.

IaaS

C.

SaaS

D.

PaaS

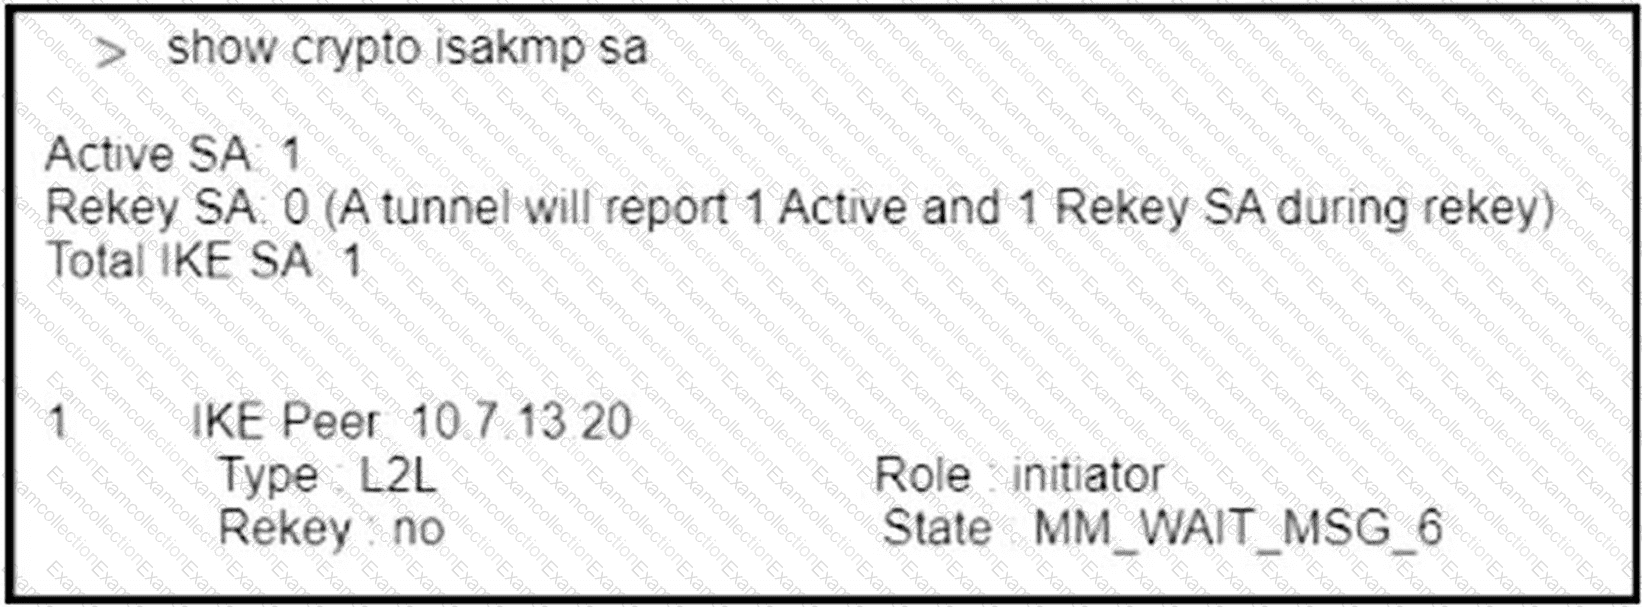
Refer to the exhibit.

During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?

A.

Configure matching peer-identity values under each tunnel group on both endpoints.

B.

Add the same pre-shared key on both peers within their tunnel-group attributes.

C.

Implement identical Diffie-Hellman group numbers within the active IKEv1 policy.

D.

Apply equivalent transform sets and lifetimes inside the crypto-map entries.

What is the difference between a site-to-site VPN and a remote-access VPN?

A.

A site-to-site VPN connects a private network using software endpoints, and a remote-access VPN connects devices to user resources in the network.

B.

A site-to-site VPN uses a Cisco GET VPN configuration, and a remote-access VPN uses a virtual tunnel interface configuration.

C.

A site-to-site VPN uses a GRE over IPsec configuration, and a remote-access VPN uses a Cisco GET Transport VPN configuration.

D.

A site-to-site VPN connects two private networks behind VPN termination devices, and a remote-access VPN connects a user to a private network.

Which attack is preventable by Cisco ESA but not by the Cisco WSA?

A.

buffer overflow

B.

DoS

C.

SQL injection

D.

phishing

An engineer is implementing DHCP security mechanisms and needs the ability to add additional attributes to profiles that are created within Cisco ISE Which action accomplishes this task?

A.

Define MAC-to-lP address mappings in the switch to ensure that rogue devices cannot get an IP address

B.

Use DHCP option 82 to ensure that the request is from a legitimate endpoint and send the information to Cisco ISE

C.

Modify the DHCP relay and point the IP address to Cisco ISE.

D.

Configure DHCP snooping on the switch VLANs and trust the necessary interfaces

Which feature requires that network telemetry be enabled?

A.

per-interface stats

B.

SNMP trap notification

C.

Layer 2 device discovery

D.

central syslog system

An engineer is adding a Cisco DUO solution to the current TACACS+ deployment using Cisco ISE. The engineer wants to authenticate users using their account when they log into network devices. Which action accomplishes this task?

A.

Configure Cisco DUO with the external Active Directory connector and tie it to the policy set within Cisco ISE.

B.

Install and configure the Cisco DUO Authentication Proxy and configure the identity source sequence within Cisco ISE

C.

Create an identity policy within Cisco ISE to send all authentication requests to Cisco DUO.

D.

Modify the current policy with the condition MFASourceSequence DUO=true in the authorization conditions within Cisco ISE

What is the benefit of installing Cisco AMP for Endpoints on a network?
A.

It provides operating system patches on the endpoints for security.

B.

It provides flow-based visibility for the endpoints network connections.

C.

It enables behavioral analysis to be used for the endpoints.

D.

It protects endpoint systems through application control and real-time scanning