Cisco 350-701 - Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT†and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?
Which two actions does the Cisco identity Services Engine posture module provide that ensures endpoint security?(Choose two.)
Why is it important to implement MFA inside of an organization?
What is the Cisco API-based broker that helps reduce compromises, application risks, and data breaches in an environment that is not on-premise?
Why is it important for the organization to have an endpoint patching strategy?
An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.
The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of
certificate should be presented to the end-user to accomplish this goal?
What is an advantage of using a next-generation firewall compared to a traditional firewall?
On Cisco Firepower Management Center, which policy is used to collect health modules alerts from managed
devices?
Which feature is configured for managed devices in the device platform settings of the Firepower Management
Center?
Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize
applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?
For which two conditions can an endpoint be checked using ISE posture assessment? (Choose two)
Which functionality does Incident Manager provide in Cisco XDR?
Refer to the exhibit.
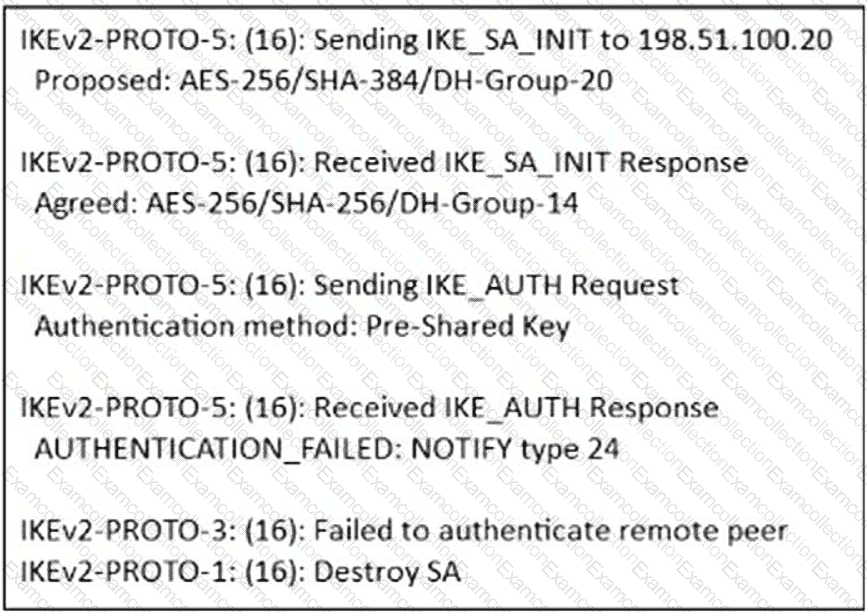
A site-to-site IKEv2 VPN between a Cisco Secure Firewall Threat Defense device with public IP address 203.0.113.10 and a third-party firewall with public IP address 198.51.100.20 is failing to establish at a logistics company. The engineer enables IKEv2 debugging on the FTD and captures the output. Which action must be performed to resolve the issue?
A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?
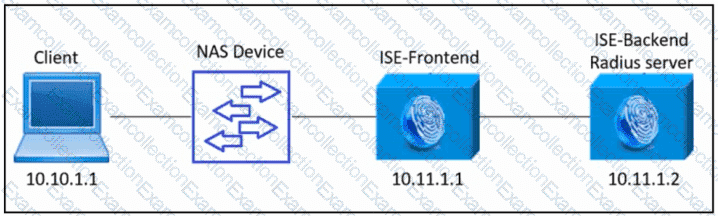
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.
Which Cisco ISE configuration must be used?