Microsoft MD-102 - Managing and Securing Microsoft 365 Endpoints by using Intune
You use the Microsoft Deployment Toolkit (MDT) to manage Windows 11 deployments.
From Deployment Workbench, you modify the WinPE settings and add PowerShell support.
You need to generate a new set of WinPE boot image files that contain the updated settings.
What should you do?
You have a Microsoft 365 E5 subscription.
You need to download a report that lists all the devices that are NOT enrolled in Microsoft Intune and are assigned an app protection policy.
What should you select in the Microsoft Endpoint Manager admin center?
You have a computer named Computed that has Windows 10 installed.
You create a Windows PowerShell script named config.psl.
You need to ensure that config.psl runs after feature updates are installed on Computer5.
Which file should you modify on Computer5?
You have a Microsoft 365 subscription that uses Microsoft Intune and contains 1,000 Windows 11 Enterprise devices.
Users sign in to the devices as standard users.
You have a PowerShell remediation that contains the following scripts:
script1.ps1 : Detects a machine-wide configuration value under the HKLM registry key
script2.ps1 : Corrects the configuration value
You need to ensure that script2.ps1 only runs when script1.ps1 detects an issue.
Which output should you use as a trigger?
You have a Microsoft 365 E5 subscription that contains a device named Device 1.
Device1 is Microsoft Entra joined.
You manage Device1 by using Microsoft Intune.
You need to use a remote action to reset the device as quickly as possible. If the device is turned off. the action must resume after the device is powered on.
Which remote action should you use?
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Microsoft Intune to manage devices.
You have a Windows 11 device named Device1 that is enrolled in Intune. Device1 has been offline for 30 days.
You need to remove Device1 from Intune immediately. The solution must ensure that if the device checks in again, any apps and data provisioned by Intune are removed. User-installed apps, personal data, and OEM-installed apps must be retained.
What should you use?
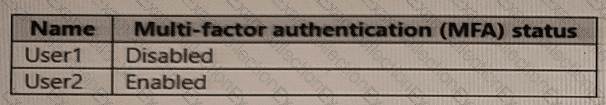
You have an Azure AD tenant that contains the users shown in the following table.
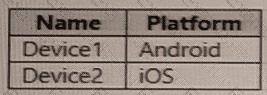
You have the devices shown in the following table.
You have a Conditional Access policy named CAPolicy1 that has the following settings:
• Assignments
o Users or workload identities: User 1. User1
o Cloud apps or actions: Office 365 Exchange Online
o Conditions: Device platforms: Windows, iOS
• Access controls
o Grant Require multi-factor authentication
You have a Conditional Access policy named CAPolicy2 that has the following settings:
Assignments
o Users or workload identities: Used, User2
o Cloud apps or actions: Office 365 Exch
o Conditions
â– Device platforms: Android, iOS
â– Filter for devices
â– Device matching the rule: Exclude filtered devices from policy
â– Rule syntax: device. displayName- contains " 1 "
â– Access controls
â– Grant Block access
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
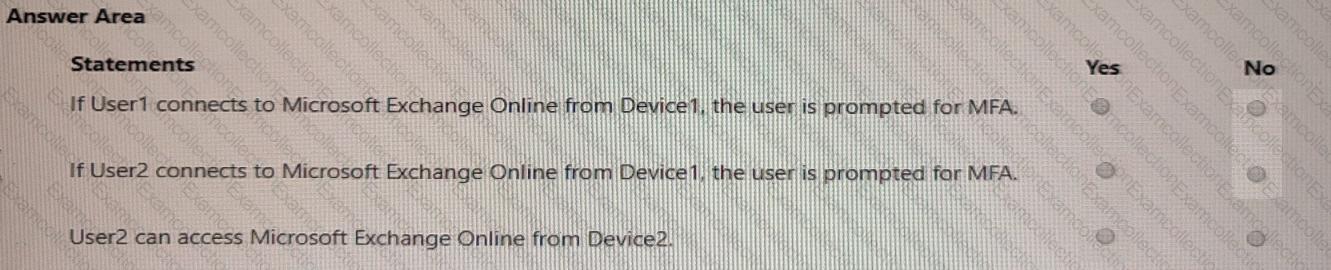
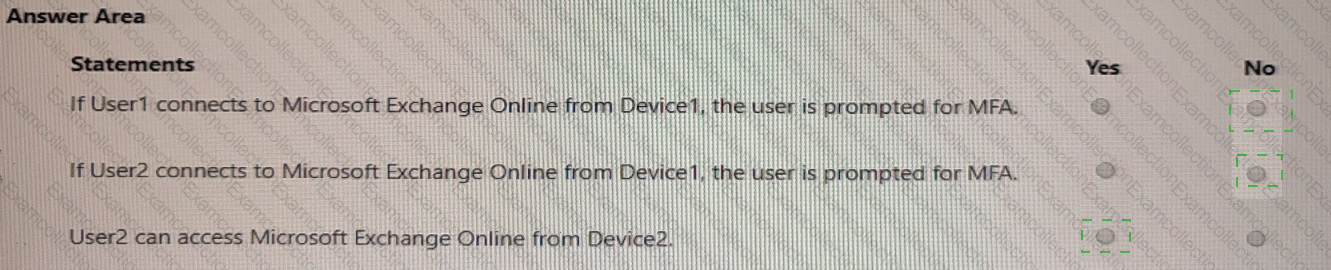
You have a Microsoft 365 E5 subscription and a computer that runs Windows 11.
You need to create a customized installation of Microsoft 365 Apps for enterprise.
Which four actions should you perform in sequence? To answer, move the appropriate cmdlets from the list of cmdlets to the answer area and arrange them in the correct order.
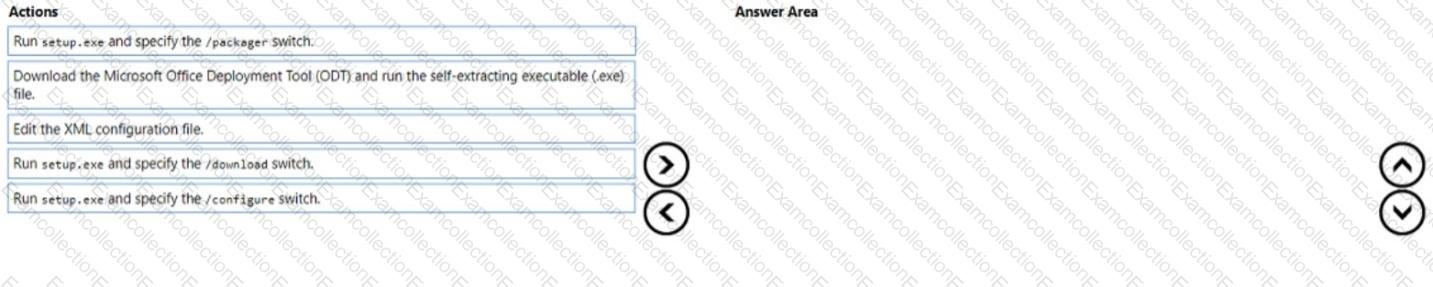
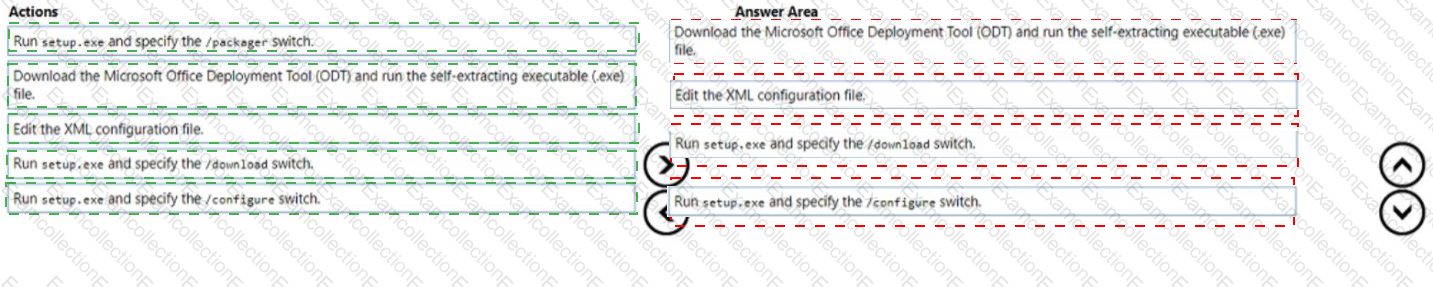
You have a Hyper-V host that contains the virtual machines shown in the following table.
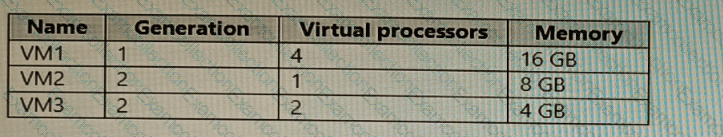
On which virtual machines can you install Windows 11?
You have a Microsoft Entra tenant that contains the users shown in the following table.
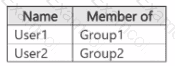
You have devices enrolled in Microsoft Intune as shown in the following table.
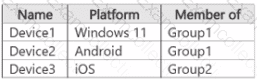
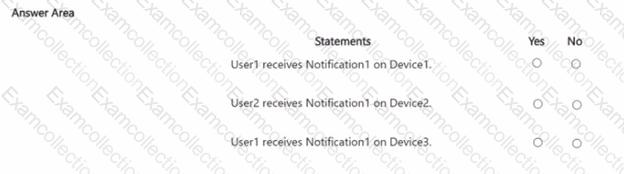
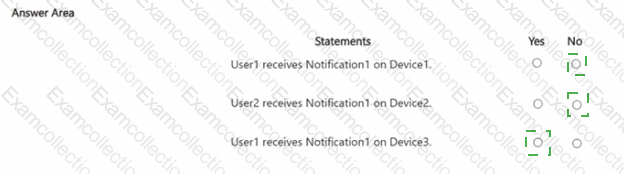
From Intune, you create and send a custom notification named Notification! to Group1. For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.