Fortinet NSE7_SOC_AR-7.6 - Fortinet NSE 7 - Security Operations 7.6 Architect
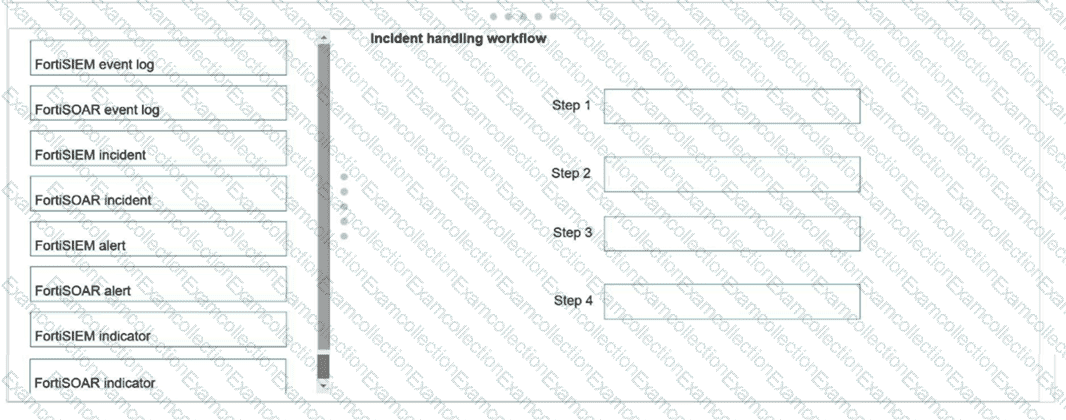
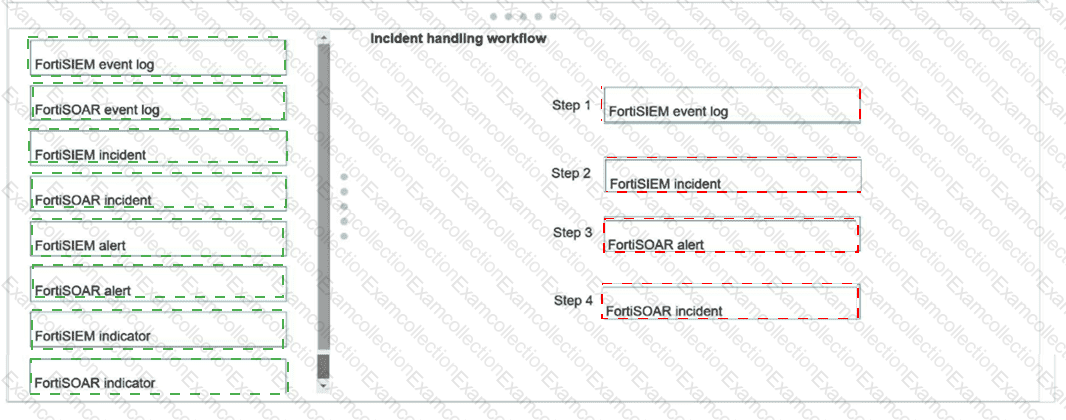
Using the default data ingestion wizard in FortiSOAR, place the incident handling workflow from FortiSIEM to FortiSOAR in the correct sequence. Select each workflow component in the left column, hold and drag it to a blank position in the column on the right. Place the four correct workflow components in order, placing the first step in the first position at the top of the column.
Which FortiAnalyzer feature uses the SIEM database for advance log analytics and monitoring?
You are using FortiSIEM analytics to reference the configuration management database (CMDB) event type categories with the following requirements:
Attribute: Event Type
Value: Group: Logon Success
Which operator must you use for the analytics search? Choose one answer.
Which two playbook triggers enable the use of trigger events in later tasks as trigger variables? (Choose two.)
Based on the Pyramid of Pain model, which two statements accurately describe the value of an indicator and how difficult it is for an adversary to change? (Choose two answers)
Refer to the Exhibit:
An analyst wants to create an incident and generate a report whenever FortiAnalyzer generates a malicious attachment event based on FortiSandbox analysis. The endpoint hosts are protected by FortiClient EMS integrated with FortiSandbox. All devices are logging to FortiAnalyzer.
Which connector must the analyst use in this playbook?
A partner organization recently suffered a distributed denial-of-service (DDoS) attack, but the adversary’s identity and TTPs remain unknown. Your SOC has not received any relevant threat intelligence from the partner organization, but you are asked to determine whether similar activity could be happening in your environment. Which threat hunting action should you perform first? Choose one answer.
Refer to the exhibit.
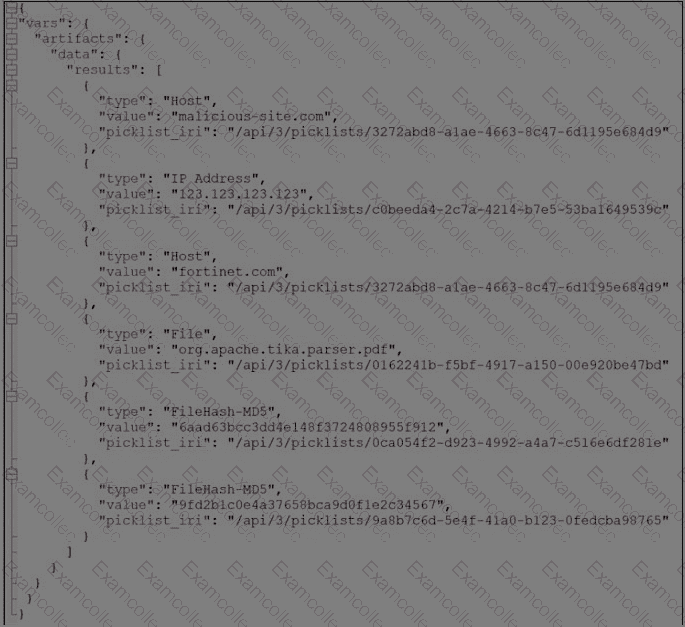
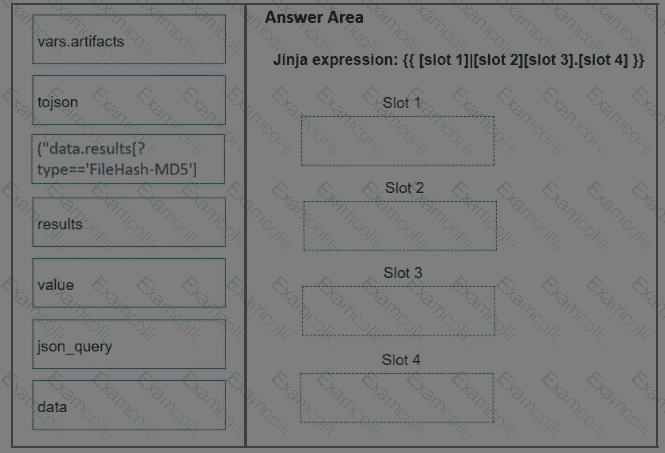
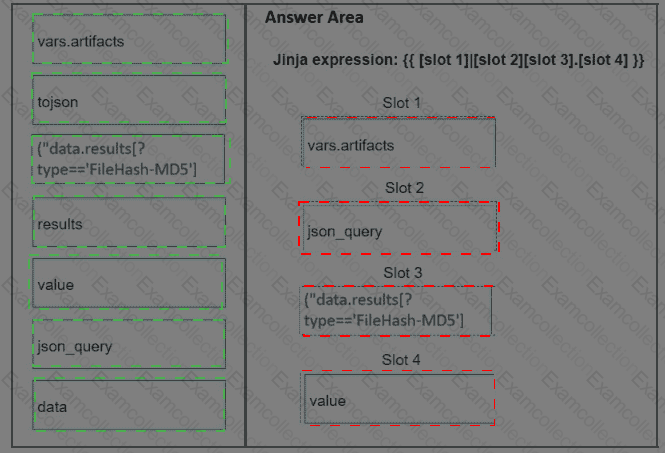
What is the correct Jinja expression to filter the results to show only the MD5 hash values?
{{ [slot 1]|[slot 2] [slot 3].[slot 4] }}
Select the jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first
step in the first slot. Once you place an expression, you can move it again if you want to change your answer before moving to the next question. You
need to drop four jinja expressions in the work area.
Select and drag the screen divider to change the viewable area of the source and work areas.