Fortinet NSEI_OTS_AR-7.6 - Fortinet NSE I - OT Security 7.6 Architect
Refer to the exhibit.
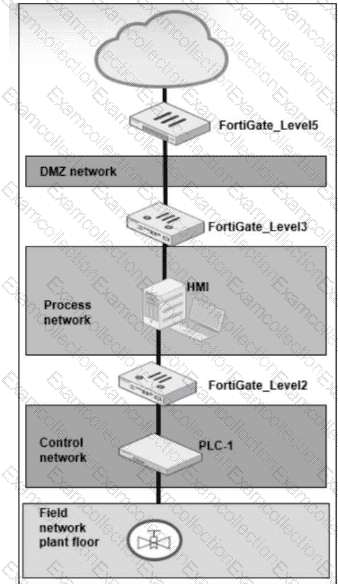
A simplified OT network is shown. You want to optimize the protection of this OT network. Which two controls must you implement? (Choose two answers)
Refer to the exhibit.
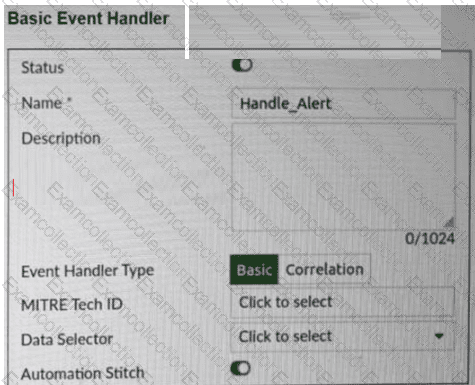
A basic event handler is shown. You have enabled Automation Stitch to automate the handling of an alert. Which two steps must you take to use this automation stitch? (Choose two answers)
Refer to the exhibit.

Based on the information provided on the partial Event Monitor page shown in the exhibit, how was the attack detected? (Choose one answer)
Refer to the exhibit.
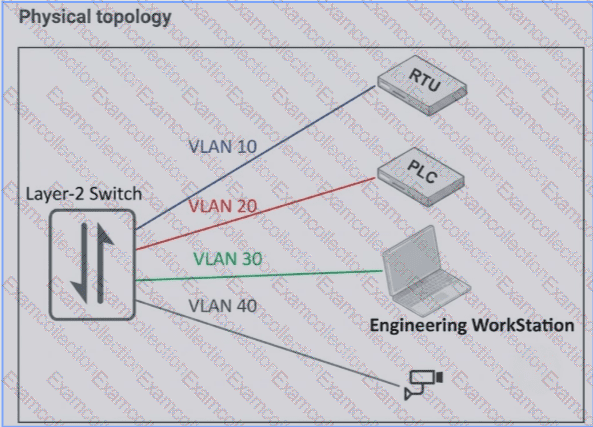
A partial OT network is shown. You have configured the FortiGate device with VLANs to segment the OT network. The supervisor now wants to connect to the PLC from the Engineering Workstation. How can you allow access from the Engineering Workstation to the PLC? (Choose one answer)
Refer to the exhibit.
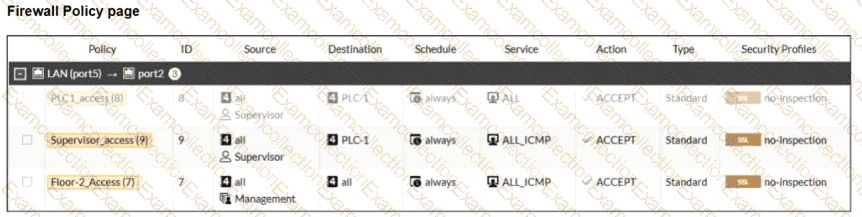
The configuration of firewall policies is shown.
To improve the security of your OT network, you have configured authentication in the firewall policies as shown in the exhibit, with CLI parameters set to their default settings. However, when you test HTTPS access from the LAN subnet to PLC-1, it is successful without any authentication prompt.
What is the reason?
Refer to the exhibit.
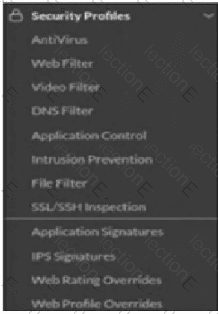
The OT devices behind the ruggedized FortiGate have vulnerabilities and you want to apply a virtual patching profile in the firewall policy. Why is Virtual Patching not available in the Security Profiles section? (Choose one answer)