


Microsoft SC-100 - Microsoft Cybersecurity Architect
You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.
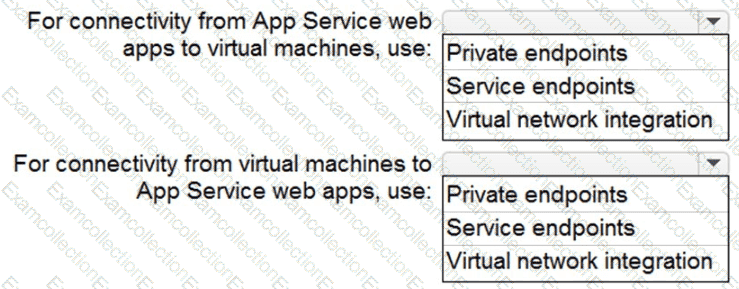
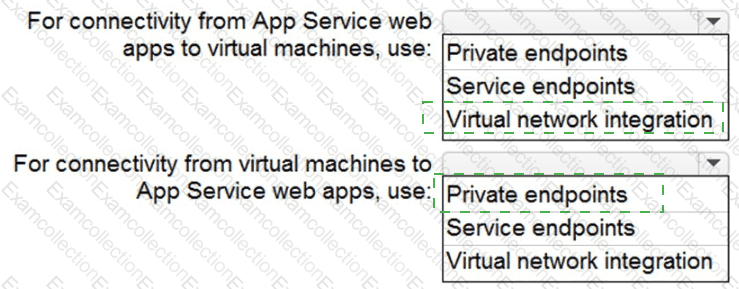
You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
You have multiple Azure subscriptions that each contains multiple resource groups.
You need to identify the privileged role assignments in each subscription and any associated security risks. The solution must minimize administrative effort.
What should you use?
You have on-premises Windows 11 devices that have the Global Secure Access client deployed.
You have a Microsoft 365 subscription that uses Microsoft SharePoint Online and Exchange Online.
You deploy Microsoft Entra Internet Access from the on-premises network to Microsoft 365. The deployment has the Microsoft 365 profile enabled and contains the following:
• Default traffic policies for Microsoft 365 services
• A linked Conditional Access policy that performs compliant network checks with continuous access evaluation and is applied to all users
• An assignment to all the devices
• An assignment to a remote network associated with the on-premises network
Which Microsoft 365 resources are protected by using continuous access evaluation?
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk
• Blocks user access to Saas apps that Microsoft has identified as high risk
Solution: From the Microsoft Defender portal, you set Web content filtering to On and create a web content filtering policy. Does this meet the goal?
You have an Azure subscription that contains the Azure Virtual Machine Scale Sets shown in the following table.
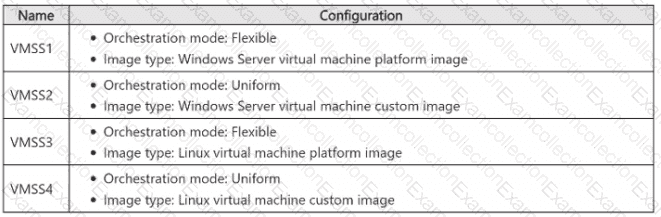
You ate evaluating Azure Update Manager and automatic virtual machine guest patching. Which virtual machine scale sets will automatic guest patching support?
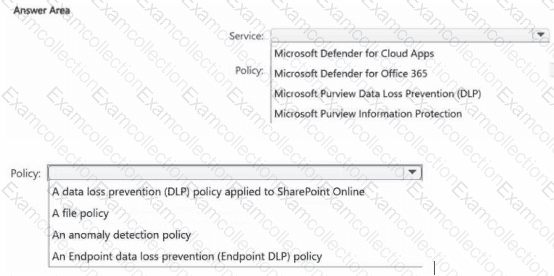
You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR and Microsoft Purview.
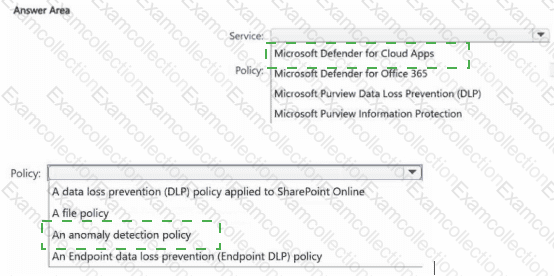
You need to recommend a data protection solution. The solution must ensure that you can identify users that download atypical amounts of data from Microsoft SharePoint Online.
Which service should you include in the recommendation, and which policy should be configured? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft 365 ES subscription. The subscription contains 500 devices that run Windows 11 Pro and are enrolled in Microsoft Intune You need to evaluate the use of Microsoft Defender Vulnerability Management to provide recommended configuration changes for the devices. Which Endpoint security settings should you use to review the recommended changes?
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender, Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
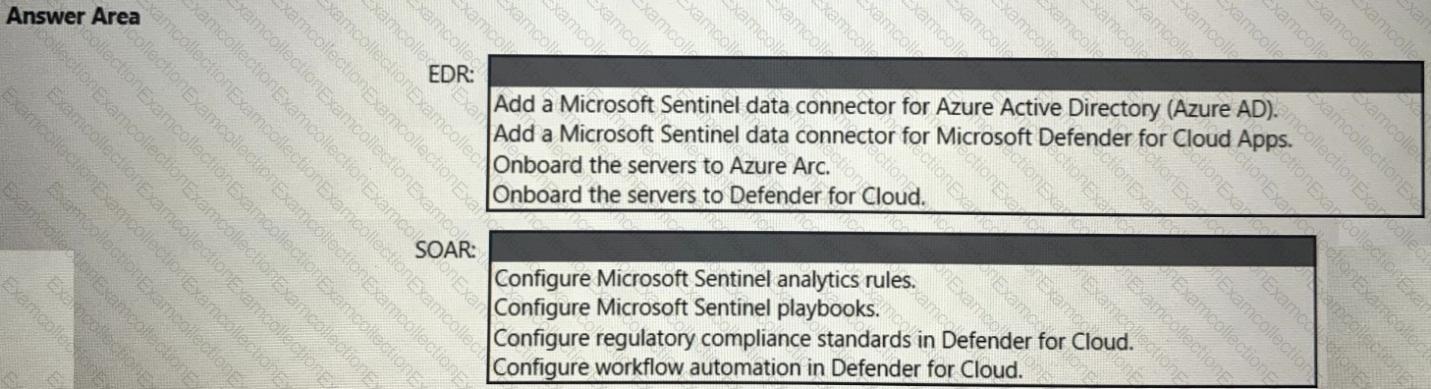
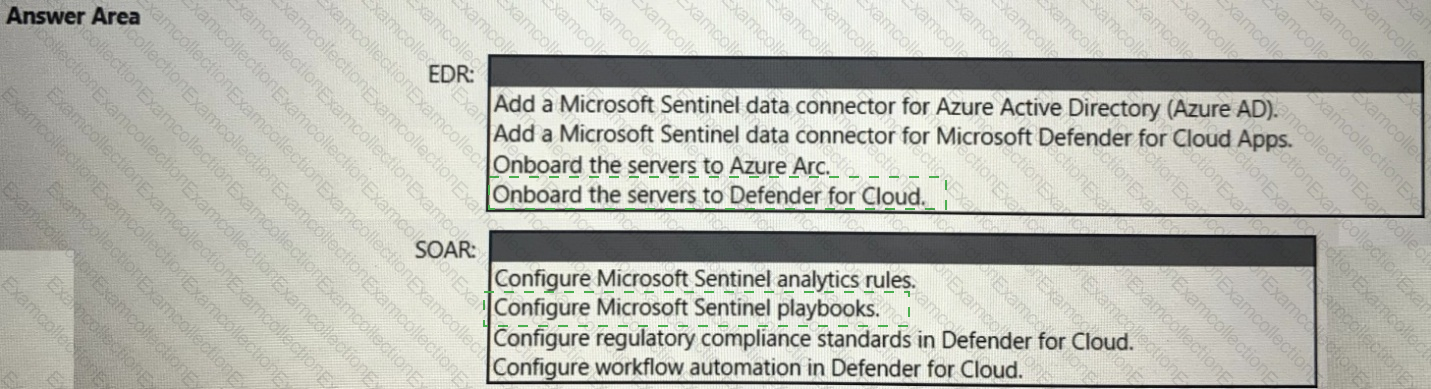
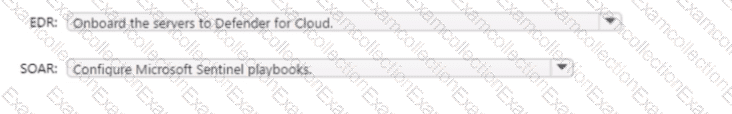
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Your company has a Microsoft 365 subscription and uses Microsoft Defender for Identity.
You are informed about incidents that relate to compromised identities.
You need to recommend a solution to expose several accounts for attackers to exploit. When the attackers attempt to exploit the accounts, an alert must be triggered. Which Defender for Identity feature should you include in the recommendation?
