Microsoft SC-500 - Microsoft Certified: Cloud and AI Security Engineer Associate
You have a Microsoft Entra tenant that uses Microsoft Entra Agent ID.
You have multiple Microsoft Foundry agents that have agent identities assigned.
You discover that one of the identities is flagged as high risk due to unusual sign-in activity.
You need to ensure that agent access to resources is restricted automatically based on risk.
What should you create?
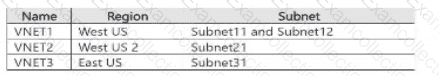
The subscription contains the virtual machines shown in the following table.
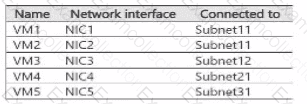
On Nl1I, you configure an application security group named ASG1.
On which other network interfaces can you configure ASG1?
You have an Azure subscription that contains the following servers:
•200 virtual machines that run either Windows Server or Ubuntu Server
•50 Azure Arc enabled servers
You use Azure Policy to manage compliance across all the servers.
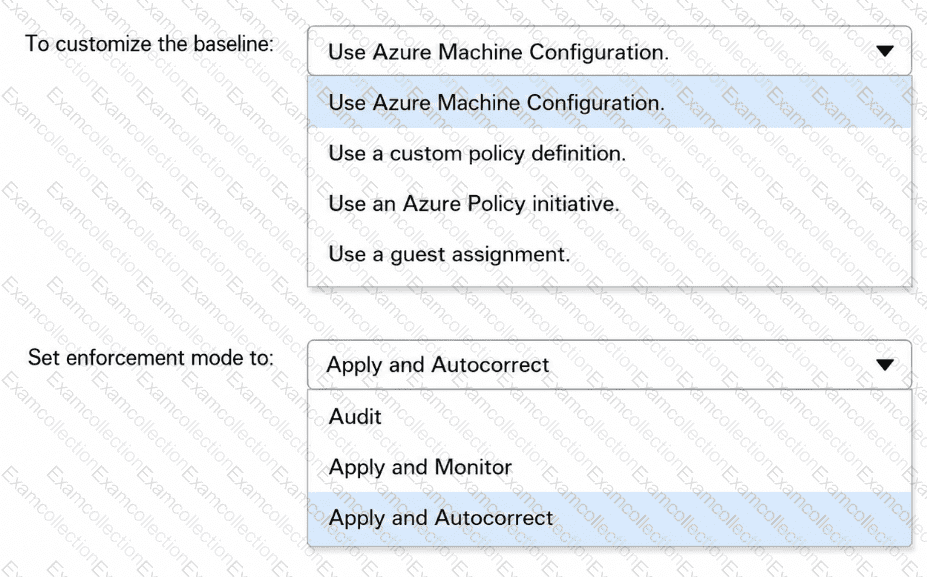
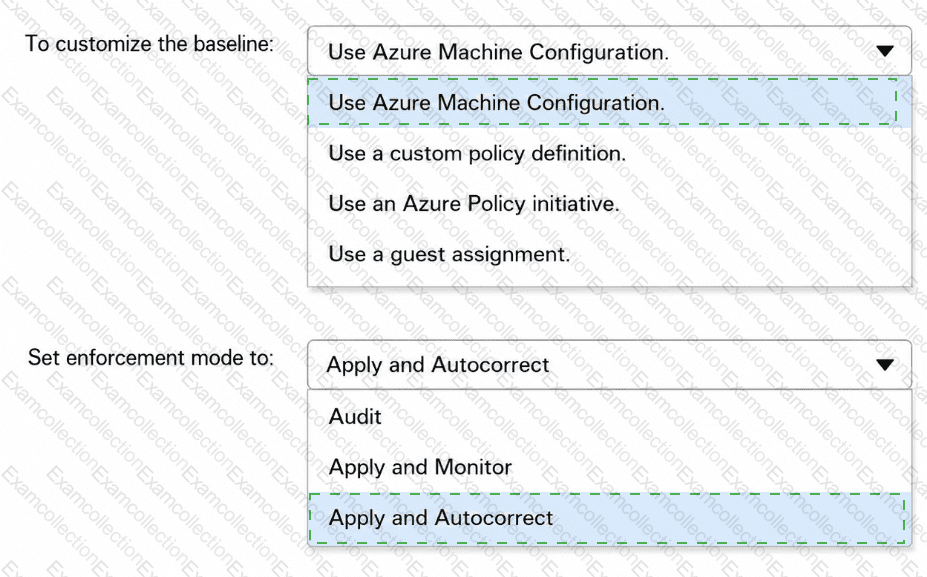
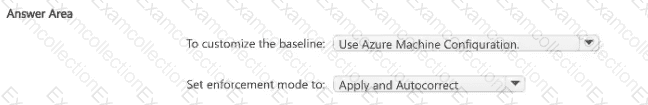
You need to enforce an organization-specific security baseline. The solution must meet the following requirements:
•Customize a built-in security baseline.
•Ensure that configuration changes to the servers are enforced automatically after the security baseline is deployed.
♦Minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have a Microsoft Entra tenant that uses Privileged Identity Management (PIM).
You need to modify the AI Administrator role settings to meet the following requirements:
•Elevated access must be evaluated by another administrator before it is granted
•Privileged access must be removed automatically after a fixed period.
Which two settings should you configure? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that has the Microsoft Defender for Cloud Foundational Cloud Security Posture Management (CSPM) plan enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud for posture management.
In Defender for Cloud, security recommendations for the resources in Azure and AWS have a risk level of Not evaluated.
You need to ensure that Defender for Cloud assigns a risk level to the recommendations.
What should you do?
You have an Azure Storage account named storage1 that contains a file share named share1.
You need to ensure that data access requests to storage1 are accepted only when authorized by Microsoft Entra ID.
What should you do?
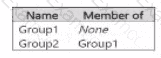
You have an Azure subscription that is linked to a Microsoft Entra tenant the tenant contains the groups shown in the following table.
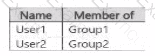
The tenant contains the users shown in the following table.
The subscription contains the Azure SOL servers shown in the following table.
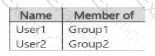
The servers are configured for Microsoft Entra-only authentication.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
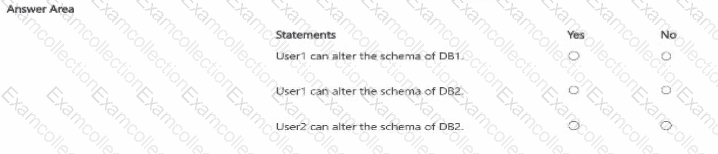
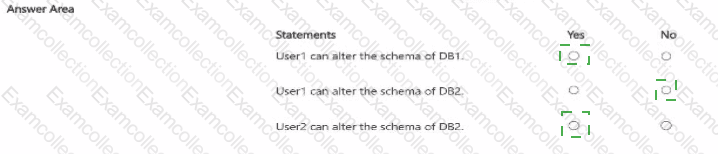
HOTSPOT
You have an Azure subscription that contains two users named User1 and User2 and the following blob containers:
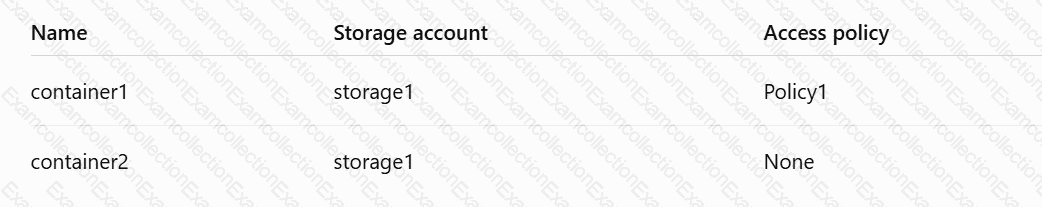
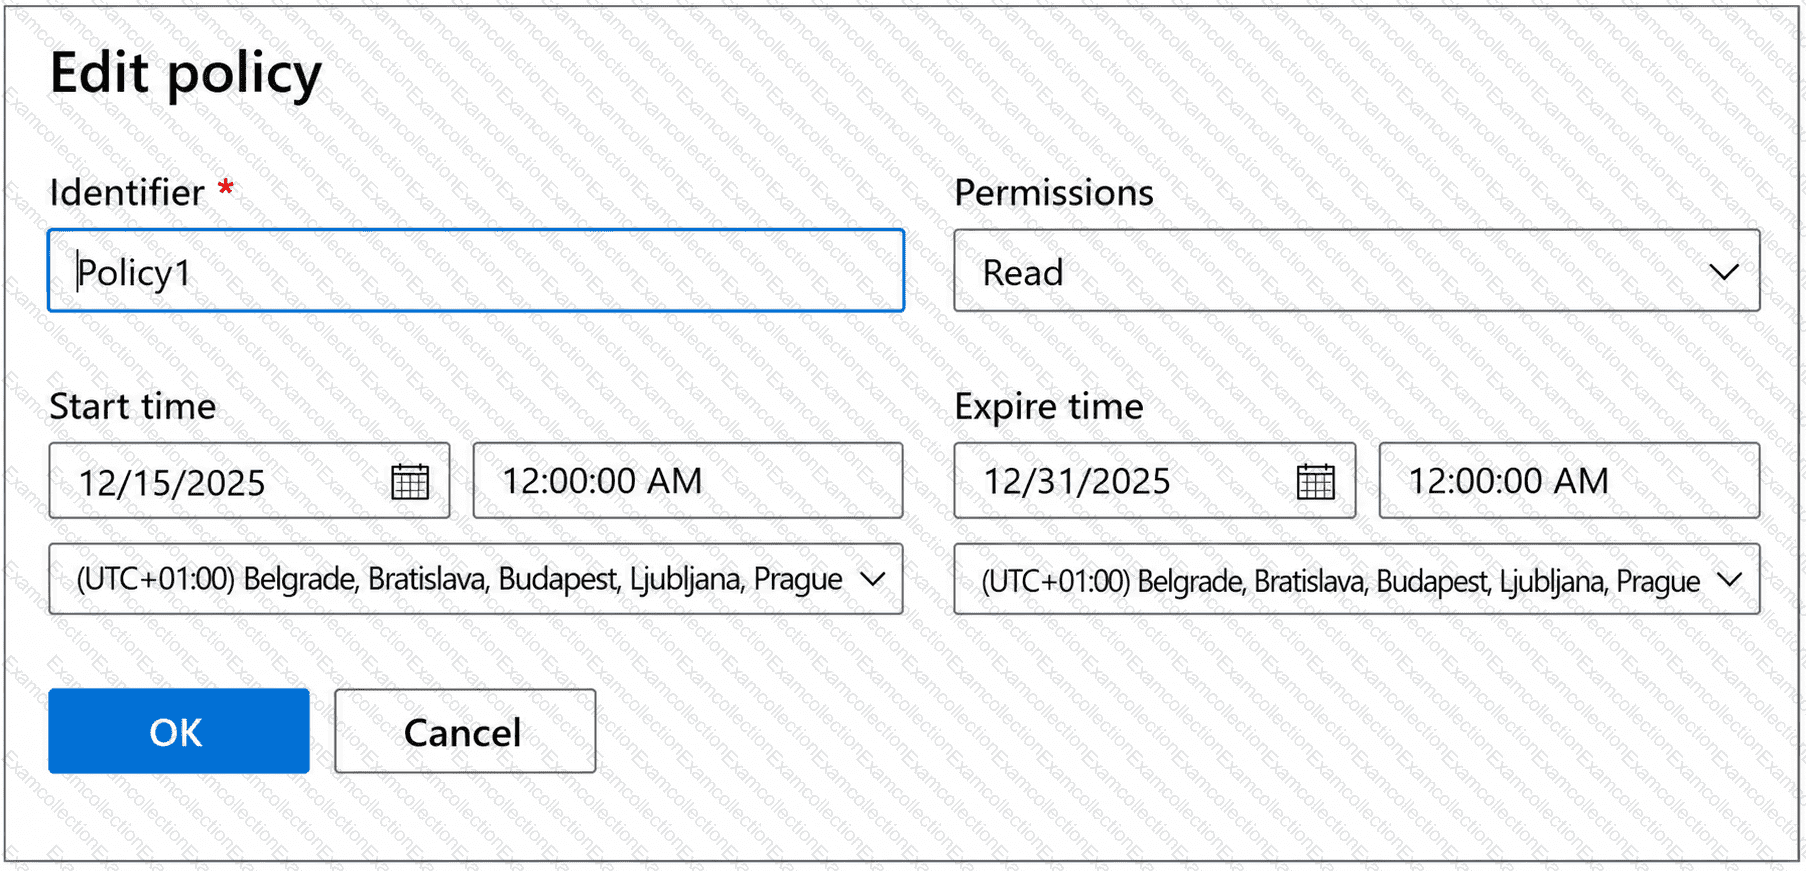
Policy1 is configured with:
Permission: Read
Start: 12/15/2025
Expiry: 12/31/2025
Role assignments on storage1:
User1 → Storage Blob Data Reader
User2 → Contributor
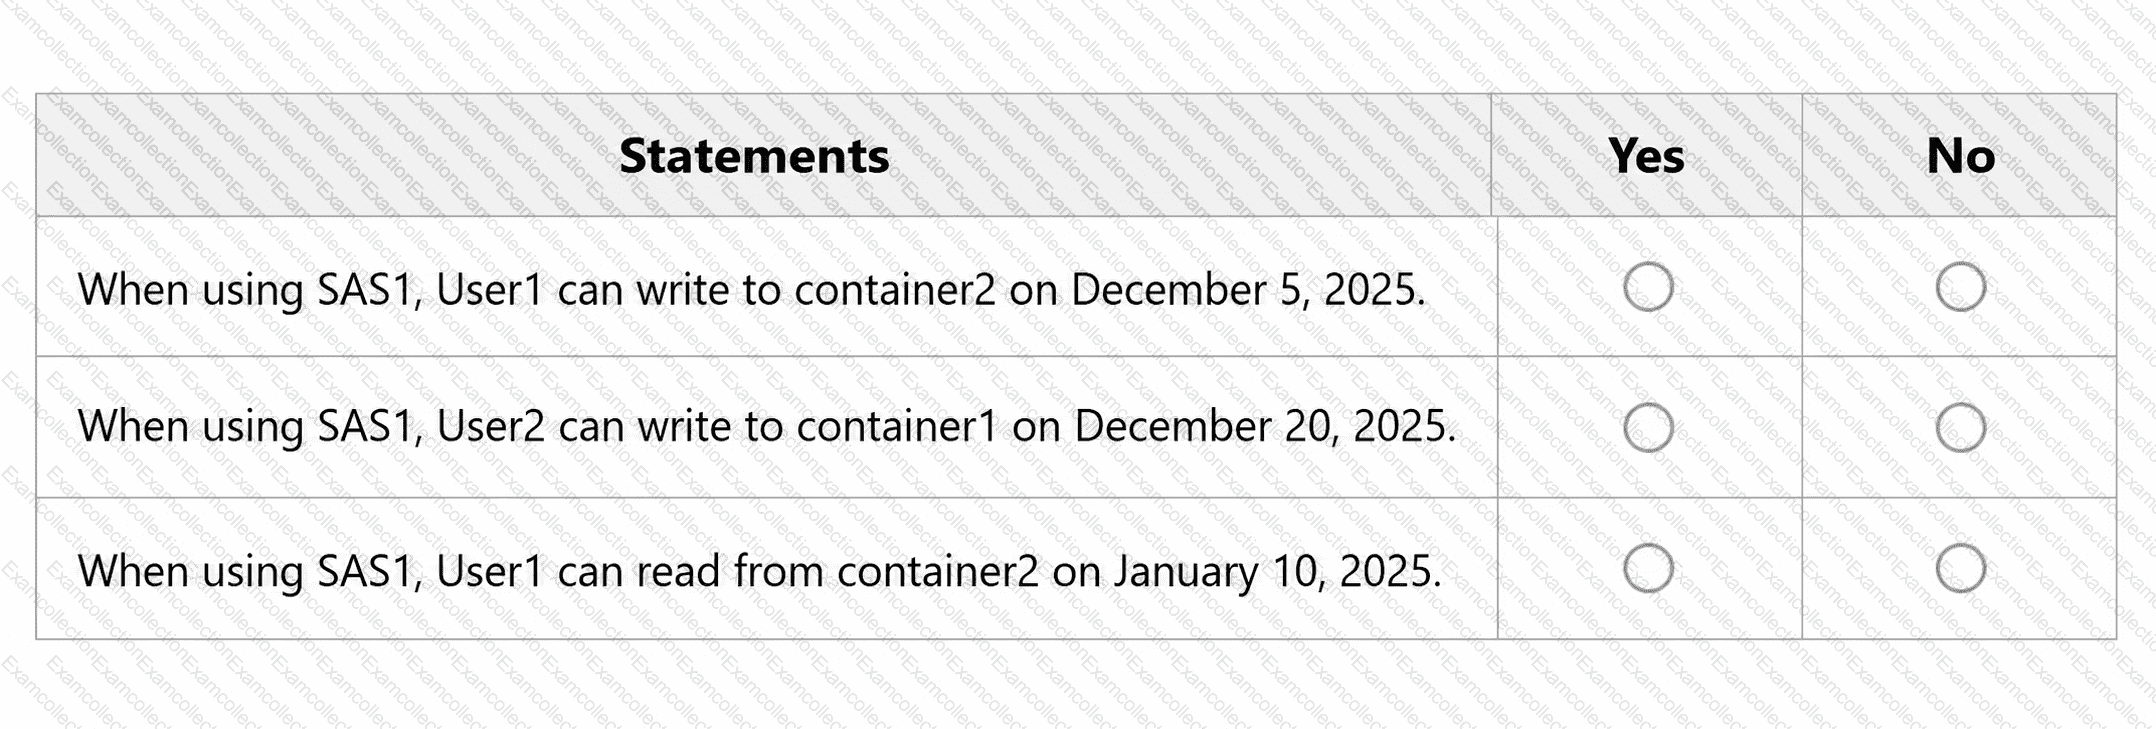
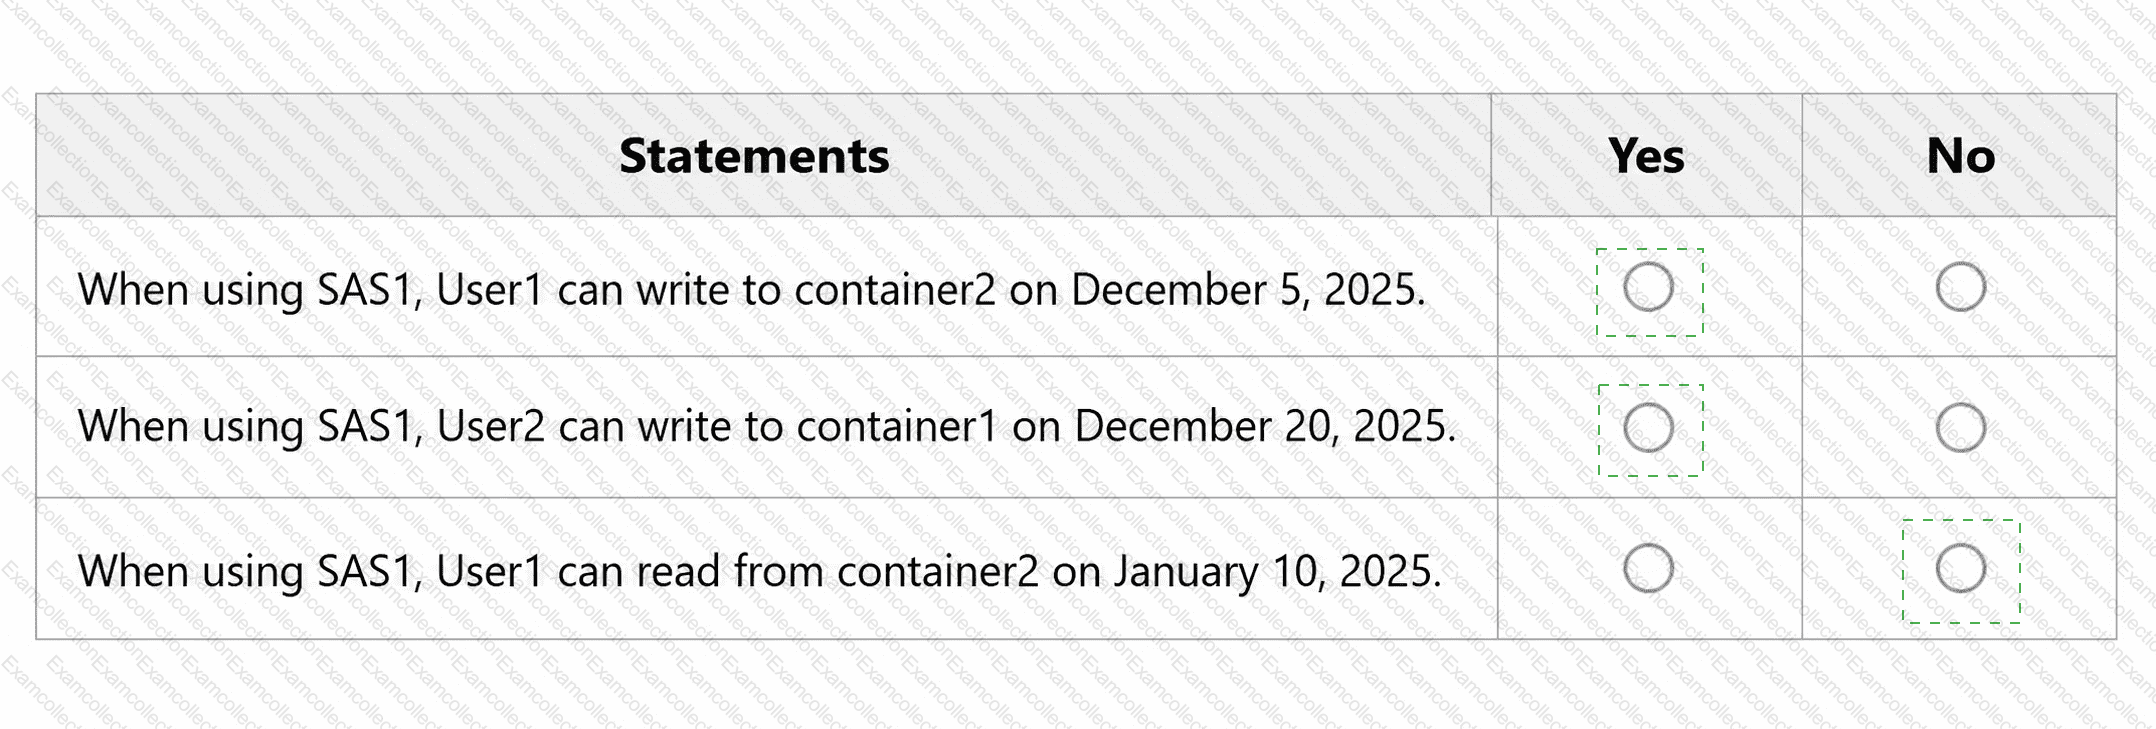
storage1 also has an account SAS named SAS1 with:
Allowed services: Blob
Allowed resource types: Container
Allowed permissions: Read, Write, List, Add, Create
Start: 12/1/2025
Expiry: 12/31/2025
For each statement, select Yes if the statement is true. Otherwise, select No.
You have an Azure subscription that uses Microsoft Defender for Cloud.
You have accounts for the following cloud services:
Alibaba Cloud
Amazon Web Services (AWS)
Google Cloud Platform (GCP)
What can you add to Defender for Cloud?
You have an Azure virtual network named VNet1 that contains a subnet named Subnet! A network security group named NSG1 is associated with Subnet1.
Vou have a storage account named storage1.
You need to ensure that access from Subnet1 to storage! uses a private IP address in Subnet1 and ran be filtered by NSG1 Public network access to storage1 must be disabled.
What should you create?