Microsoft SC-500 - Microsoft Certified: Cloud and AI Security Engineer Associate
You have a Microsoft Sentinel workspace named Workspace1
You have 100 on-premises servers that run Linux and have the Azure Monitor Agent installed.
You need to collect Syslog events from the Linux servers. The solution must meet the following requirements:
•Ensure that filtering occurs before data is written to Workspace1
•Reduce ingestion costs by excluding low value Syslog messages.
What should you include in the solution?
You have an Azure subscription that contains a resource group named RG1 and has Microsoft Defender tor Cloud enabled.
You connect an Amazon Web Services (AWS) account to Defender for Cloud by creating the AW5 connector in RG1.
You have a Microsoft Entra group named Group1 that contains the UMf accounts of (he security analysts at your company.
You need to ensure that the members of Group1 can view multicloud recommendations and security alerts ' or the connected AWS account. The solution must follow the principle of least privilege
Which role should you assign to Group1 for RG1?
You have an Azure subscription named Sub1 that contains a storage account named storage1
Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has on-upload malware scanning enabled for a monthly cap of 10,000 GB per storage account.
You use a Microsoft Sentinel workspace to monitor security events on all Azure resources.
You need to configure storage1 to use a malware scanning cap of 2.000 GB per month.
What should you do?
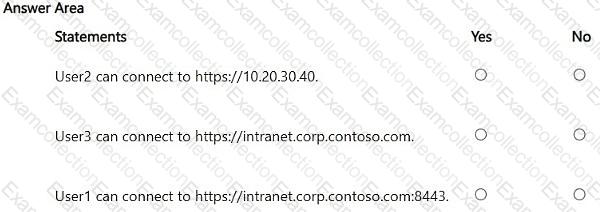
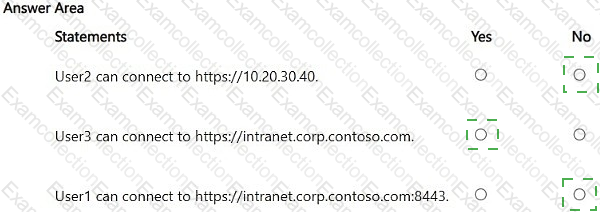
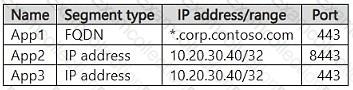
You have three on-premises apps named App1, App2, and App3 that are configured in Microsoft Entra Private Access as shown in the following table.
You have the users shown in the following table.
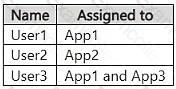
The Global Secure Access client is deployed to all user devices.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.